
Researchers have discovered two potentially serious vulnerabilities in wireless LAN devices that they say are often used in airplanes.
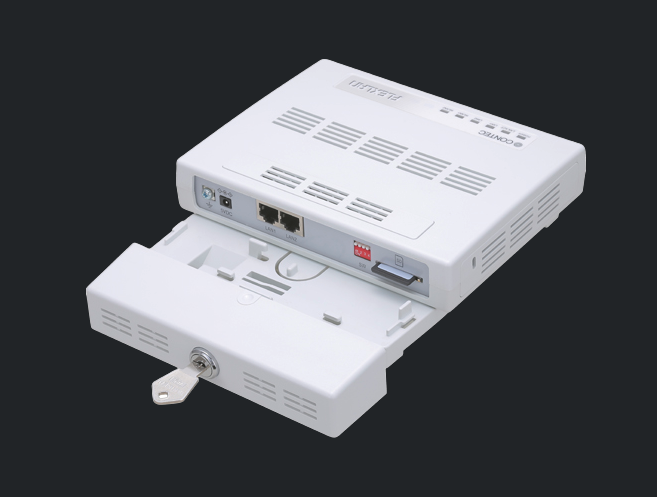
Researchers Thomas Knudsen and Samy Younsi of Necrum Security Labs identified the vulnerabilities in the Flexlan FX3000 and FX2000 series wireless LAN devices made by Contec, a Japan-based company that specializes in embedded computing, industrial automation, and IoT communication technology.
One of the security holes, CVE-2022-36158, is related to a hidden webpage that can be used to execute Linux commands on the device with root privileges. The device’s web-based management interface does not provide a link to this hidden page.
“From here we had access to all the system files but also be able to open the telnet port and have full access on the device,” the researchers explained in a blog post.
The second vulnerability, CVE-2022-36159, is related to a backdoor account and the use of a weak hardcoded password. The researchers found a root user account with a default hardcoded password that is likely designed for maintenance purposes. The password is stored as a hash, but it was quickly cracked by the experts. An attacker can use this account to gain control of the device.
Contec says its Flexlan wireless LAN devices are ideal for use in distribution systems, factories, offices and with embedded devices.
However, the researchers say they are often used in airplanes for Wi-Fi access points that passengers can use to connect to the internet and in-flight services.
Aircraft manufacturers and in-flight entertainment system vendors have always maintained that hacker attacks on passenger-accessible systems do not pose a risk to flight controls and safety due to isolation of the systems.
However, malicious actors could still find these types of vulnerabilities useful, as shown by researchers in the past.
Younsi told SecurityWeek that the flaws they have found could be exploited by a passenger, as the vulnerable interface is accessible. The attacker could, for example, collect the data of other passengers or deliver malware to their devices.
“We can imagine a scenario where a malicious actor can spoof the HTTPS traffic by uploading his own certificate in the router to see all requests in clear text,” the researcher explained. “Another scenario would be to redirect the traffic to a malicious APK or iOS application to infect the mobile phone of each passenger.”
In its own advisory, the vendor said “there are possibilities of data plagiarism, falsification, and system destruction with malicious programs if this vulnerability was exploited by malicious attackers.”
Contec explained that the vulnerabilities are related to a private webpage that developers can use to execute system commands, and this page is not linked to from settings pages available to users.
Firmware versions 1.16.00 for FX3000 series and 1.39.00 for FX2000 series devices address the vulnerabilities.
The US Cybersecurity and Infrastructure Security Agency (CISA) did recently publish an advisory describing vulnerabilities in a Contec medical device, but it has not released an advisory for the Flexlan issues. Japan’s JPCERT/CC did release an advisory this month.
The affected devices are not used only in airplanes. Nihon Kohden, a Japanese manufacturer of medical electronic equipment, issued a statement recently to inform customers about these vulnerabilities, saying that it’s investigating the impact on its products and systems.
Related: Threat Actors Start Exploiting Meeting Owl Pro Vulnerability Days After Disclosure
Related: Vulnerabilities in Realtek Wi-Fi Module Expose Many Devices to Remote Attacks







You must be logged in to post a comment Login