
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Latest Cybersecurity News

Hackers accessed its online shopping platform and stole customers’ personal and payment card information.

The top payout is for high-impact architectural research demonstrating full administrative control.

The extension performed host reconnaissance and attempted to create a reverse SSH tunnel.

The attackers used offensive agentic techniques to access the company’s systems and internal tools.

DebugBear says its DNS records were compromised via its domain registrar, and early findings show a single customer was targeted.

The FBI has officially pinned the $6 billion Binance hack on North Korea’s TraderTraitor as the attackers launder the stolen crypto.

CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks.

The startup maps how identities, assets and vulnerabilities connect, and uses AI agents to find and fix risky combinations of issues.

A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.

Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.

Noteworthy stories that might have slipped under the radar: Iran eyed in military freezer hacks, Copenhagen University breach, AI-powered malware.

As organizations eliminate passwords, attackers will adapt. Instead of attacking the authenticator directly, they will look for opportunities around it.

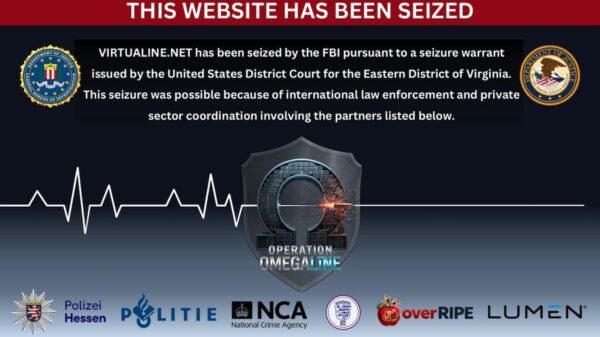
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments.

Binance hacked Binance hacked

The FBI has officially pinned the $6 billion Binance hack on North Korea’s TraderTraitor as the attackers launder the stolen crypto.

Ivanti vulnerability exploited Ivanti vulnerability exploited

CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks.

Hacker Hacker

A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.

Top Cybersecurity Headlines

Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.

Drupal says a highly critical Commerce Core access bypass is exploited in the wild and urges store owners to audit their orders.

Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds.

SecurityWeek Industry Experts

More Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Close the security gaps between pentests. Join this session to explore agentic pentesting and gain a practical framework for continuous exposure validation in your CTEM program.

Register

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register
Upcoming Cybersecurity Events

SecurityWeek’s CodeSecCon 2026 will bring together developers and cybersecurity professionals to revolutionize the way applications are built, secured, and maintained.
[Originally August 19, 2026]
Learn More
Zero Trust Summit Now On-Demand

SecurityWeek’s 2026 Zero Trust Summit will deep-dive into the world of digital identity management and the role of zero-trust principles and associated technologies
[Originally October 14, 2026]
Read More
CISO Forum Virtual Summit

The 2026 Virtual CISO Forum brings together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.
[November 10 & 11, 2026 | Virtual]
Read More
Cyber AI and Automation Summit 2026

SecurityWeek’s Cyber AI & Automation Summit pushes the boundaries of security discussions by exploring the implications and applications of predictive AI, machine learning, and automation in modern cybersecurity programs.
[December 8 & 9, 2026 | Virtual]

Read More

Vulnerabilities

Cybercrime

Shortly after a few Pakistani websites were defaced, the Pakistan Cyber Army (PCA) responded with a massive defacement campaign focusing on China, less than 24-hours after taking out 26 Bangladeshi government domains. As is the case with most defacements from the PCA, or similar groups, the motive is mostly entertainment – unless there is a chance for political propagandizing. According to messages left by the PCA, it would see that propaganda was the aim this time around.

In February of 2008, two backup tapes containing data maintained by the U.S. Secret Service were left behind on a DC Metrorail. Now, nearly five years after the fact, the Department of Homeland Security's Office of Inspector General (DHS-OIG) is launching an investigation into the incident.

Researchers from Rapid7 and the Shadowserver Foundation discovered something unique last week. While browsing files on USENET, they discovered a botnet that has thousands of endpoints, and was able to operate without detection for months. To make matters worse, the botmaster took to Reddit earlier this year in order to brag about it.

Rapid7 on Friday released Metasploit Pro 4.5, the latest version of its flagship penetration testing and security risk assessment tool. The new release brings capabilities that let organizations simulate social engineering attacks and help understand just how vulnerable they may be to phishing attacks.

When I was a boy growing up in New Jersey, the basement in our older family home would flood several times a year. It was on a concrete slab and usually dried out after a few days, so it was okay. I came home from college one weekend and upon hearing my mom say she was going to carpet the basement, I reminded her of the periodic floods. She looked me in the eye and said, "Dammit Alan, I’m doing...

In what appears to be another case of the FBI taking credit for cracking a case they created, a former sailor is being charged with attempted espionage, after he allegedly tried to deliver naval secrets to the Russian Federation.

LONDON - A British student was on Thursday convicted for his role in a series of cyber-attacks by the hacking group Anonymous that cost the US online payments giant PayPal millions of dollars. Christopher Weatherhead, 22, was found guilty of participating in attacks by Anonymous on PayPal, MasterCard and other companies that refused to process payments to the whistleblowing website WikiLeaks.

Before arriving at Apple this fall, Kristin Paget used to break things at Microsoft. Now, her job will be to help secure Mac OS X for Apple, as the company that was once blasé about security starts to take things seriously. Paget’s LinkedIn profile lists her as working at Apple since September 2012 as a “Core OS Security Researcher”.

RIM is planning to release BlackBerry 10, the latest edition of its mobile operating system, on Jan. 30, and with that release comes an unmentioned security feature – password blocking. RIM hasn’t officially announced the protection settings, but a BlackBerry site in the U.K. discovered a list of 106 passwords that are forbidden on the new mobile OS.

Microsoft is planning to release seven security bulletins to close out the year. Five of the bulletins are rated 'Critical', while the other two are classified as 'Important.' All totaled, the bulletins address 11 vulnerabilities affecting Microsoft Word, Windows, Office, Windows Server and Internet Explorer (IE). The two 'Important' bulletins both address issues in Windows.

As the world races to adopt cloud computing, there is still a nagging challenge for IT security professionals: How can applications and infrastructure be trusted and controlled when organizations have seemingly given up both to their cloud providers? With Forrester Research forecasting public cloud computing to reach $57 billion in 2013 and exploding to over $157 billion by 2020, IT security needs to find an approach that works or risk becoming marginalized.

According to a recent study sponsored by ID Experts on patient and data security, 94% of healthcare organizations surveyed said they have suffered at least one data breach. This figure, the report says, demonstrates that uphill battle that the healthcare industry faces when it comes to information security. Further, the study says that such security problems cost healthcare organizations an estimated $7 billion annually.

Working with international law enforcement in the U.K., Canada, Romania, and the Czech Republic, the U.S. Department of Justice has issued arrest warrants for seven individuals said to have been involved in a multimillion dollar scam that targeted Internet marketplace websites.

Event image poster

The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.

Learn More

Application Security

Application Security

OSS Scanner sends unreviewed, model-generated vulnerability reports to open source maintainers that opt in.

Cloud Security

Cloud Security

The top payout is for high-impact architectural research demonstrating full administrative control.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.