
CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks.

A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.

Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.

As organizations eliminate passwords, attackers will adapt. Instead of attacking the authenticator directly, they will look for opportunities around it.

Risk managers are trained to spot weak signals, plan for disruption and make hard decisions under uncertainty. But the discipline looks different when the risk is not a system or an enterprise, but you.

The process that gates nearly every B2B deal is a self-assessment the sender distrusts and the receiver accepts. There is finally a better basis for trust between companies.

Keep your patch management pipelines primed in case another round of Citrix NetScaler patches get released soon.

Where your developers sit on the AI adoption scale has a real impact on how you are addressing security risk.
Close the security gaps between pentests. Join this session to explore agentic pentesting and gain a practical framework for continuous exposure validation in your CTEM program.
RegisterJoin as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.
Register
SecurityWeek’s CodeSecCon 2026 will bring together developers and cybersecurity professionals to revolutionize the way applications are built, secured, and maintained.
[Originally August 19, 2026]
SecurityWeek’s 2026 Zero Trust Summit will deep-dive into the world of digital identity management and the role of zero-trust principles and associated technologies
[Originally October 14, 2026]
The 2026 Virtual CISO Forum brings together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.
[November 10 & 11, 2026 | Virtual]
SecurityWeek’s Cyber AI & Automation Summit pushes the boundaries of security discussions by exploring the implications and applications of predictive AI, machine learning, and automation in modern cybersecurity programs.
[December 8 & 9, 2026 | Virtual]
-

CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks. (November 2, 2026)
-

Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week. (October 30, 2026)
-


Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution. (October 30, 2026)
-


Drupal says a highly critical Commerce Core access bypass is exploited in the wild and urges store owners to audit their orders. (October 30, 2026)
-


The FBI has officially pinned the $6 billion Binance hack on North Korea’s TraderTraitor as the attackers launder the stolen crypto. (November 2, 2026)
-

A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities. (October 31, 2026)
-
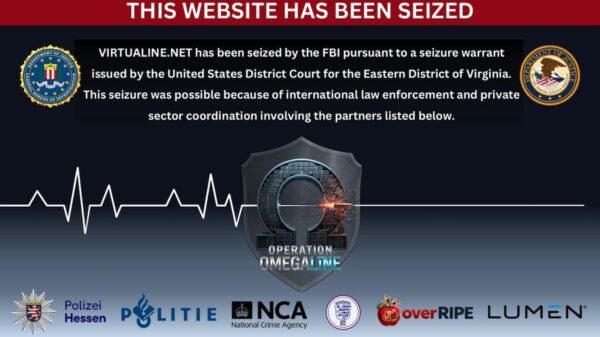
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments. (October 30, 2026)
-


Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds. (October 30, 2026)