
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Management & Strategy

Over 50 New CVE Numbering Authorities Announced in 2022

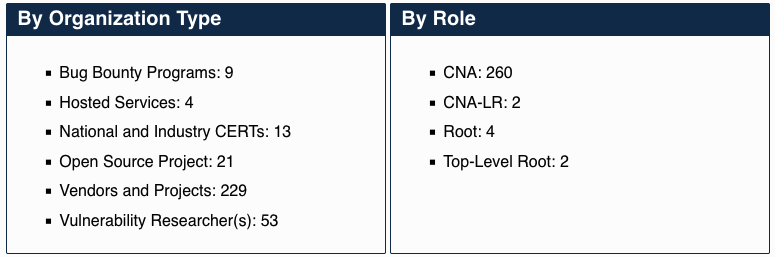
More than 50 organizations have been added as a CVE Numbering Authority (CNA) in 2022, bringing the total to 260 CNAs across 35 countries.

Most CNAs can assign CVE identifiers to vulnerabilities found in their own products, but some can also assign CVEs to flaws found by their researchers in third-party software that is not in another CNA’s scope.
More than 50 organizations have been added as a CVE Numbering Authority (CNA) in 2022, bringing the total to 260 CNAs across 35 countries.

Most CNAs can assign CVE identifiers to vulnerabilities found in their own products, but some can also assign CVEs to flaws found by their researchers in third-party software that is not in another CNA’s scope.

2022 CVE Numbering AuthoritySecurityWeek has conducted an analysis of announcements made by the CVE Program and found that 54 CNAs were added in 2022, compared to 43 in 2021.

The 2022 list includes cybersecurity companies such as Proofpoint, Bugcrowd, Qualys, CyberArk, Green Rocket Security, Dragos, SailPoint, Senhasegura, NetRise, HYPR, and Netskope.

Major tech companies such as Baidu, Canon, Google (open source software), Seagate, Unisoc, GE Healthcare, Philips, Medtronic, Baxter Healthcare, and Citrix are now also CNAs.

Major industrial solutions providers such as General Electric (Gas Power), Honeywell, and Rockwell Automation can now also assign CVEs to vulnerabilities.

There are also some national organizations and nonprofits that have joined the list of CNAs, including the Dutch Institute for Vulnerability Disclosure (DIVD), Automotive Security Research Group, Slovakia’s National Cyber Security Centre (SK-CERT), and the National Cyber Security Centre in the Netherlands (NCSC-NL).

Advertisement. Scroll to continue reading.

The list of new CNAs also includes Docker, WolfSSL, Grafana Labs, Honor, Zowe, OneKey, KrakenD, Dual Vipers, Baicells, HashiCorp, OpenCloudOS, OpenNMS Group, Crestron Electronics, OpenHarmony, Full Services, KNIME, OpenGauss Community, Hitachi and Hitachi Vantara, Hallo Welt, OpenAnolis, ZUSO Advanced Research Team, Go Project, JetBrains, The Missing Link Australia (TML), and the OpenBMC Project.
CNA

Related: Moussouris: U.S. Should Resist Urge to Match China Vuln Reporting Mandate

Related: Over 28,000 Vulnerabilities Disclosed in 2021

Related: Microsoft: China Flaw Disclosure Law Part of Zero-Day Exploit Surge

Related: GitHub Introduces Private Vulnerability Reporting for Public Repositories

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Cohere has appointed Jaya Baloo as CISO.

Jensen Huang has resigned as President and Chief Executive Officer at NVIDIA.

Sean Sweeney has become CIO of the City of Charleston, South Carolina.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





