
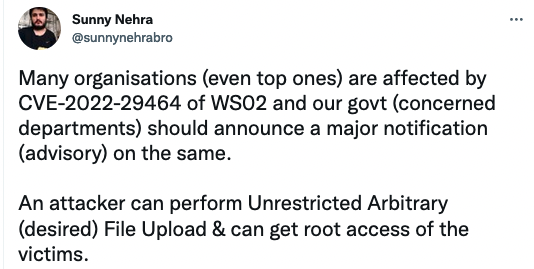
Products made by enterprise software development solutions provider WSO2 are affected by a critical vulnerability that has been exploited in the wild.
According to WSO2’s website, its products are used by many major companies worldwide, including Fortune 500 firms, which could all be at risk.
In addition, the US Cybersecurity and Infrastructure Security Agency (CISA) on Monday added the flaw to its Known Exploited Vulnerabilities Catalog and instructed federal agencies to install the available patches until May 16.
The security hole is tracked as CVE-2022-29464 and it impacts WSO2’s API Manager, Identity Server, Enterprise Integrator, and Open Banking products. In its advisory for CVE-2022-29464, the vendor said temporary mitigations were made available in January 2022 and fixes were delivered in February.
The vulnerability, discovered by Orange Tsai from DEVCORE, who over the past years has discovered many critical bugs that ended up being exploited in attacks, has been described as an arbitrary file upload issue that can lead to remote code execution.
“Due to improper validation of user input, a malicious actor could upload an arbitrary file to a user controlled location of the server. By leveraging the arbitrary file upload vulnerability, it is further possible to gain remote code execution on the server,” WSO2 said in its advisory.
Technical details and proof-of-concept (PoC) exploits are available for the vulnerability and Rapid7 on Friday reported seeing opportunistic exploitation in the wild.
“Attackers appear to be staying close to the original proof-of-concept exploit and are dropping web shells and coin miners on exploited targets,” Rapid7 said, noting that exploitation is “quite easy.”
Threat intelligence company Bad Packets has also reported seeing exploitation attempts.
In addition to the WSO2 bug, CISA added six other flaws to its Known Exploited Vulnerabilities Catalog, which is often referred to as a “Must-Patch” list, due to the fact that government agencies are required — and private organizations are advised — to immediately address these vulnerabilities.
The most recent issues added to the list are two Windows bugs (CVE-2022-26904 and CVE-2022-21919) and the Linux kernel flaw named Dirty Pipe.
Related: CISA’s ‘Must Patch’ List Puts Spotlight on Vulnerability Management Processes
Related: CISA Adds 14 Windows Vulnerabilities to ‘Must-Patch’ List







You must be logged in to post a comment Login