The Ohio Lottery has confirmed being targeted in a cyberattack and a ransomware group claims to have stolen a significant amount of information from the organization’s systems.
The Ohio state lottery informed customers on its website that it has experienced a “cybersecurity event”. The organization assured the public that its gaming system is fully operational, but said it decided to shut down some key systems to contain the incident.
Tickets can still be purchased, but winning numbers and jackpots for some games are not available on the Ohio Lottery website and mobile app. In addition, the mobile cashing app and Super Retailer locations are not cashing prizes greater than $599 as a result of the incident.
A seemingly new ransomware group named DragonForce took credit for the attack on December 27.
The hackers claim to have stolen more than 600 Gb of data from the Ohio Lottery, including databases storing over three million records associated with employees and players. The data allegedly includes names, email and postal addresses, winnings, dates of birth, and social security numbers.

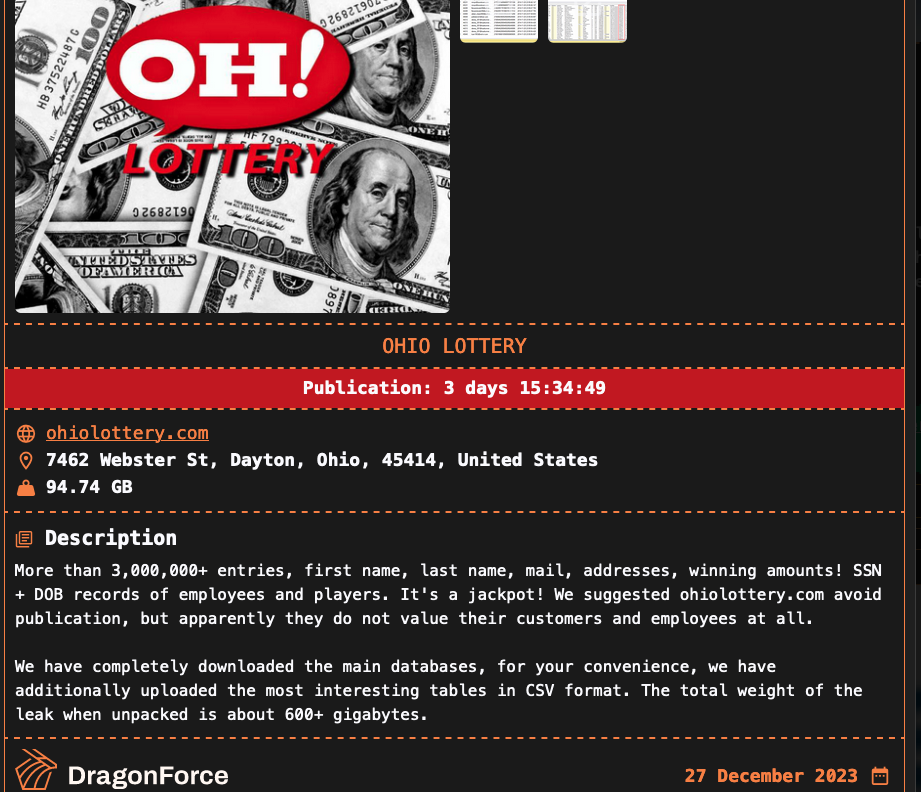
The cybercriminals published several screenshots to demonstrate their claims. They are threatening to make all the stolen data public in three days, suggesting that the Ohio Lottery is not willing to pay the demanded ransom.
DragonForce’s leak website currently lists 21 victims. The group has become one of the most active ransomware gangs.
Related: Ransomware Group Claims 100 Gb of Data Stolen From Nissan
Related: BlackCat Strikes Back: Ransomware Gang “Unseizes” Website, Vows No Limits on Targets
Related: Inmate, Staff Information Stolen in Rhode Island Prison Data Breach














