
Consumer groups voiced dismay Friday after a US Senate panel considering privacy legislation scheduled a largely industry-packed witness list for an upcoming hearing.



Hi, what are you looking for?

Consumer groups voiced dismay Friday after a US Senate panel considering privacy legislation scheduled a largely industry-packed witness list for an upcoming hearing.
California Attorney General Xavier Becerra and Assemblymember Marc Levine last week introduced a new piece of legislation that would require organizations to notify consumers if their passport or biometric information has been compromised in a data breach.
Federal prosecutors have recommended a sentence of nearly three years in prison for a former Virginia high school teacher convicted of hacking into private digital accounts of celebrities and others.
Duo Labs, part of Cisco-owned Duo Security, has launched a new service designed to analyze Chrome extensions and deliver security reports on them.
Several phone apps are sending sensitive user data, including health information, to Facebook without users' consent, according to a report by The Wall Street Journal.An analytics tool called "App Events" allows app developers to record user activity and report it back to Facebook, even if the user isn't on Facebook, according to the report .
Key parts of the internet infrastructure face large-scale attacks that threaten the global system of web traffic, the internet's address keeper warned Friday.
The Face ID and Touch ID authentication feature introduced recently to WhatsApp for iOS can be easily bypassed, but a patch has been released.
Entrust Datacard and Thales have signed a definitive agreement for Entrust to acquire the nCipher general purpose hardware security module (GP HSM) division of Thales. Financial details have not been disclosed.
Cybercriminals say they are willing to pay over a million dollars per year to individuals with network management, penetration testing, and programming skills willing to put on a black hat, a new Digital Shadows report reveals.
A major mobile ad fraud operation impacts millions of users through infected consumer applications, Oracle reveals.
Pulse Secure, a company that specializes in secure access solutions, this week unveiled a new software defined perimeter (SDP) product designed to provide organizations direct secure access to their resources and applications.
A researcher says he has discovered yet another critical cross-site scripting (XSS) vulnerability in Yahoo Mail. The recently patched flaw could have been exploited to steal the targeted user’s emails and attach malicious code to their outgoing messages.
Mexico’s privacy watchdog said Wednesday that the federal Attorney General’s Office stonewalled it for more than a year as it tried to investigate the government’s use of powerful Israeli spyware against journalists, lawyers and activists.
Google said Wednesday it forgot to mention that it included a microphone in its Nest Secure home alarm system, the latest privacy flub by one of the tech industry’s leading collectors of personal information.
Cisco this week released patches for more than a dozen vulnerabilities across its product portfolio, including high severity flaws in HyperFlex, Prime Infrastructure, and Prime Collaboration Assurance.
Adobe on Thursday released a second fix for the Reader vulnerability tracked as CVE 2019-7089 after the researcher who discovered the flaw managed to bypass the first patch.The security hole, identified by Alex Inführ from Cure53, allows a specially crafted PDF document to send SMB requests to the attacker’s server when the file is opened.
Microsoft informed users on Wednesday that Windows servers running Internet Information Services (IIS) are vulnerable to denial-of-service (DoS) attacks that rely on malicious HTTP/2 requests.
Latest Developments in Mueller and Russian Electoral Meddling
WinRAR, the popular data compression tool utilized by over 500 million users worldwide, is affected by a serious vulnerability that can allow arbitrary code execution through specially crafted ACE archives.
Security updates released on Wednesday for the Drupal content management system (CMS) patch a “highly critical” vulnerability that can be exploited for remote code execution.

The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.




The top payout is for high-impact architectural research demonstrating full administrative control.


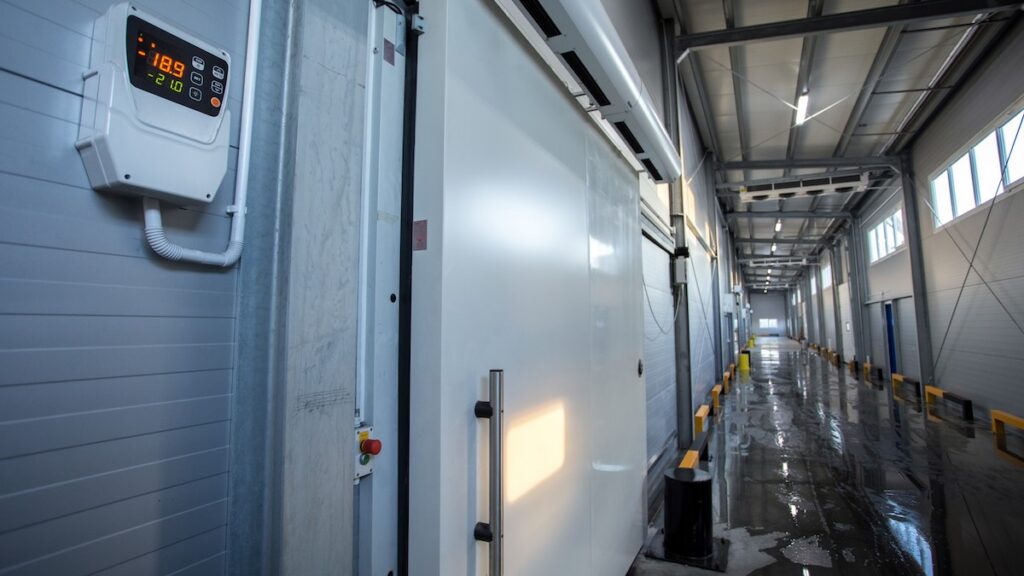
The recommendations come amid attacks targeting fridges and freezers in supermarkets and blood banks in Europe.