
A Rust-based file-encrypting ransomware was found this week to be impersonating the cybersecurity firm Sophos as part of its operation.
Dubbed ‘SophosEncrypt’, the malware is being offered under the ransomware-as-a-service (RaaS) business model, and appears to have already been used in malicious attacks.
After several security researchers warned of the new RaaS, Sophos said it was aware of the brand impersonation and that it was investigating the threat.
After analyzing a SophosEncrypt sample, Sophos revealed that the threat has capabilities beyond those typically observed in ransomware, making it “a general-purpose remote access trojan (RAT)” that can also encrypt files and generate ransom notes.
The malware, Sophos says, can communicate with its operators over email and using the Jabber instant messenger platform, and can hook the keyboard driver to log keystrokes. It also abuses WMI commands to profile the system.
“Like many other ransomware, it excludes a list of directories that would either impede the system from booting or that contain unimportant files if they were encrypted. The ransomware also checks the language settings on the system and refuses to run if it is set to use the Russian language,” Sophos explains.
According to Sophos, another SophosEncrypt sample it has identified lacks some of these non-ransomware features. Both samples, however, contain references to the same Tor (.onion) address related to a command-and-control (C&C) server, albeit none of them uses that connection.
The cybersecurity firm also discovered that both samples connect to a hardcoded IP address that has been previously associated with a Cobalt Strike C&C and with malicious attacks distributing crypto-miners.
The malware, which is executed using the Windows command line, appends the ‘.sophos’ extension to the encrypted files and drops a ransom note into each affected directory, in the form of an HTML Application (.hta) file.
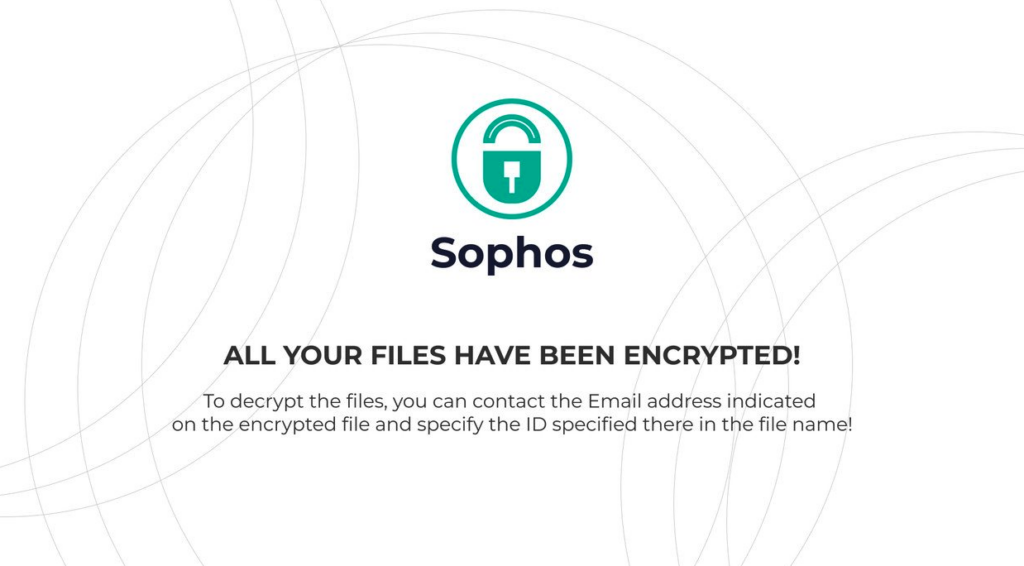
“The ransomware also retrieves a graphic from a public image library website, and uses that to change the Windows desktop wallpaper to a screen which reads ‘Sophos’. It’s notable that this does not replicate Sophos logos, colors, or branding but instead presents a green padlock logo and instructions on how the target can find and use the ransom note to contact the attackers,” Sophos explains.
Related: Japan’s Nagoya Port Suspends Cargo Operations Following Ransomware Attack
Related: Ransomware Criminals Are Dumping Kids’ Private Files Online After School Hacks
Related: TSMC Says Supplier Hacked After Ransomware Group Claims Attack on Chip Giant






