
Cloud security company Wiz has announced the launch of a new database whose goal is to keep track of vulnerabilities and other security issues affecting cloud services.
Cybersecurity researchers often find vulnerabilities in widely used cloud services offered by companies such as AWS, Microsoft and Google. While some cloud vulnerabilities don’t require any action from the user, there are situations where impacted customers do need to take certain steps, such as rotating keys.
According to Wiz, there are several problems when it comes to the disclosure and handling of cloud vulnerabilities, including that there is no standardized notification channel across service providers and CVE identifiers are in many cases not assigned, which makes it more difficult to track issues. In addition, there is no severity scoring to help users prioritize vulnerabilities, and there is no transparency into the flaws and their detection.
Wiz has been urging the community to improve the response to cloud security vulnerabilities, including by creating a public and standardized database for reporting and enumerating vulnerabilities.
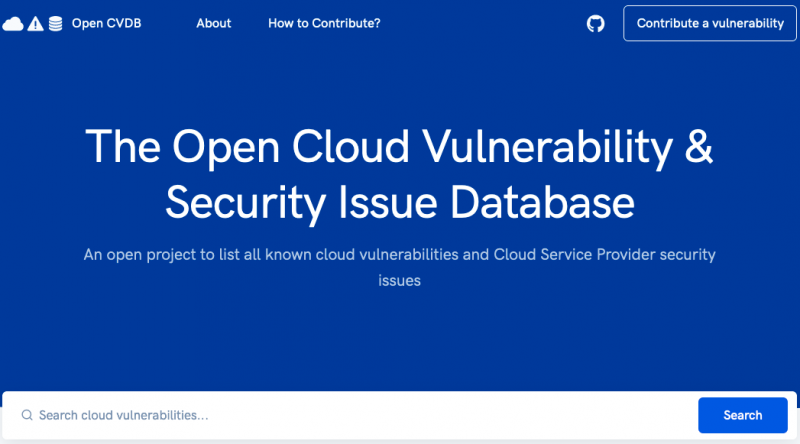
The company has now announced the launch of such a database — hosted at cloudvulndb.org — which aims to catalog all known vulnerabilities and other types of security issues affecting cloud services.
“In most cases, CSPs respond quickly to fix the security issue on their side but the lack of standardization leaves many cloud customers vulnerable and unaware of the issues in their environments,” Wiz said. “Our goal in this project is to pave the way for a centralized cloud vulnerability database, by cataloging CSP security mistakes in a new format and listing the exact steps CSP customers can take to detect or prevent these issues in their own environments.”
Wiz told SecurityWeek that currently there are nearly 70 vulnerabilities in the database, including roughly 10 critical and 10 high-severity flaws. The critical vulnerabilities are mostly cross-tenant issues, such as ChaosDB and ExtraReplica.
“Establishing metrics and a methodology for defining severity is one of the next steps in the project. In the interim, severities on the website are currently based on the site maintainers’ assessments, grounded in their cloud security expertise and history of assessing and patching cloud vulnerabilities across cloud platforms,” Wiz explained.
Each database entry contains a brief description of the vulnerability, the affected service, required remediation steps, CVEs (if there are any), disclosure date, exploitability period, detection methods, the name of the reporting researcher, and references.
The cloud vulnerabilities database is based on Scott Piper’s “Cloud Service Provider security mistakes” project — Piper will be involved in the maintenance of the Wiz-sponsored service.
Members of the cybersecurity community who want to add new entries to the database can do so by creating a pull request in a GitHub repository from where the content of the database is automatically obtained.
Any publicly known cloud security issue for which actual or potential impact has been demonstrated can be added to the database. Each entry must include required remediation actions, either by the cloud vendor or users.
Related: Researcher Awarded $10,000 for Google Cloud Platform Vulnerability
Related: Critical Code Execution Flaw Haunts VMware Cloud Director







You must be logged in to post a comment Login