
A remote attacker could log into certain NETGEAR switches and execute arbitrary code because of hardcoded credentials installed within the firmware used on the devices, CERT/CC reported last week.
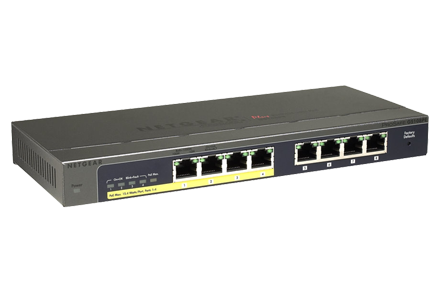
The vulnerability affects NETGEAR GS108PE ProSAFE Plus Switches, which are usually used by small businesses for managing common applications. The Power over Ethernet (PoE) features integrated into the latest models enable organizations to power devices such as IP phones and cameras, wireless access points, and Ethernet switches.
According to CERT/CC, version 1.2.0.5 of the firmware in NETGEAR GS108PE ProSAFE Plus Switches contains hardcoded credentials that enable a remote unauthenticated attacker to access the Web server running on the devices.
 By using the “ntgruser” username and the “debugpassword” password, an attacker can gain access to various software components. For example, access to produce_burn.cgi can be used to change the device’s MAC address and serial number, and new firmware can be uploaded through bootcode_update.cgi. The vulnerability can also be leveraged to manually set memory to a certain value and extract that value, CERT/CC noted in its advisory.
CERT/CC says it’s not aware of any practical solutions to address the flaw, which has been assigned the CVE identifier CVE-2014-2969. The vulnerability was reported by Marc Olivier Chouinard and its existence was disclosed to NETGEAR on May 19, 2014.
Johannes Ullrich, dean of research for the SANS Technology Institute, advises NETGEAR equipment owners to check if the username/password combination works, even if their devices have not been listed as vulnerable.
Last year, an Australian research analyzed 1.3 million compromised devices that were part of the Carna botnet. He found that in many cases the devices were hijacked after the attackers successfully authenticated by using well-known default credential combinations, such as root/root and admin/admin.
SecurityWeek has contacted NETGEAR to see if the company is planning on addressing the vulnerability, but has not heard back by press time.







You must be logged in to post a comment Login