
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Management & Strategy

Mozilla Offering Rewards for Bypassing Firefox Exploit Mitigations

Mozilla announced on Thursday that it has expanded its bug bounty program with a new category that focuses on bypass methods for the exploit mitigations, security features and defense-in-depth measures in Firefox.

Mozilla announced on Thursday that it has expanded its bug bounty program with a new category that focuses on bypass methods for the exploit mitigations, security features and defense-in-depth measures in Firefox.

Mozilla says mitigation bypasses have until now been classified as low- or moderate-severity issues, but they are now eligible for a reward associated with a high-severity flaw as part of the new Exploit Mitigation Bug Bounty.

This means a bypass mitigation with privileged access can earn researchers up to $5,000 if they submit a high-quality report. However, if the mitigation is bypassed without privileged access — this typically involves chaining more than one weakness — researchers can receive a reward for the vulnerability itself and a 50 percent bonus for the mitigation bypass.

Mozilla says it still encourages researchers to test Firefox Nightly, the testing and development version of the browser, but vulnerabilities found in Nightly will only be eligible for a bounty if they’re not found internally by Mozilla within four days of the code change that introduces the flaw being posted to the primary repository.

Some have criticized Mozilla for expanding its bug bounty program shortly after it laid off some of its cybersecurity staff. However, the company told SecurityWeek that the recent layoffs did not impact the teams responsible for the security of the Firefox browser and Firefox services.

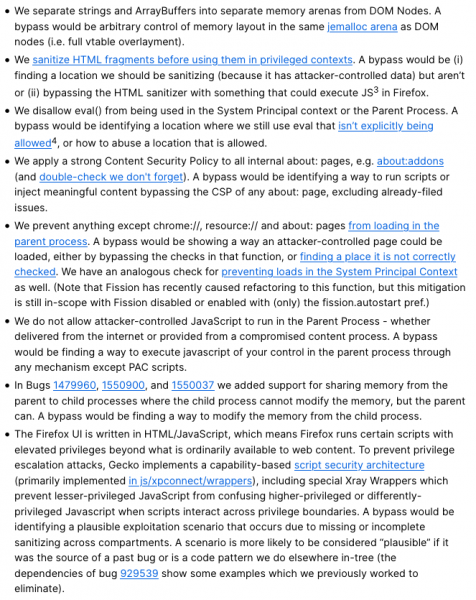
Mozilla has posted a list of the mitigations covered by the Exploit Mitigation Bug Bounty:
Advertisement. Scroll to continue reading.

Firefox exploit mitigations

Related: Firefox, IE Vulnerabilities Exploited in Attacks on China, Japan

Related: Details Released for Recently Patched Code Execution Vulnerability in Firefox

Related: Cisco Discloses Details of Chrome, Firefox Vulnerabilities

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Cohere has appointed Jaya Baloo as CISO.

Jensen Huang has resigned as President and Chief Executive Officer at NVIDIA.

Sean Sweeney has become CIO of the City of Charleston, South Carolina.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





