
A security researcher has published a proof-of-concept (PoC) exploit for the recently addressed Android zero-day vulnerability that impacts Pixel 2 devices.

Hi, what are you looking for?

A security researcher has published a proof-of-concept (PoC) exploit for the recently addressed Android zero-day vulnerability that impacts Pixel 2 devices.
Three years after Thoma Bravo acquired a majority holding in DigiCert, the Utah-based digital certificate firm has announced its acquisition by Clearlake Capital Group and TA Associates. TA already had a minority holding in the firm and has been investing in DigiCert for seven years.
Global shipping and ecommerce giant Pitney Bowes revealed on Thursday that the recent service disruptions were caused by a piece of ransomware known as Ryuk.
A northwestern Indiana hospital system is warning more than 68,000 patients that their personal information, including Social Security numbers and health records, may have been exposed during a data breach.
The head of Russia's security service said Thursday it is now reviving cooperation with US agencies over cybersecurity despite major tensions between the two countries.
October is National Cybersecurity Awareness Month (NCSAM) and an opportune time to remind every organization of the importance of “awareness” to their cybersecurity programs.
Instagram announced this week that users will have more control over the data they share with third-party applications and websites.
TA505, the Russian-speaking threat actor known for operating the Dridex Trojan and Locky ransomware, has been using a new remote access Trojan (RAT) in recent attacks, Proofpoint reports.
The city of Baltimore is set to purchase $20 million in cyber insurance coverage, five months after an attack hobbled its computer network.The city’s Board of Estimates on Wednesday approved the purchase of two $10 million policies. The premiums will total $835,000.
Russia-linked threat actor APT29 has been successfully avoiding detection for the past three years while compromising multiple government targets, ESET’s security researchers report.
Cisco on Wednesday informed customers that some of its Aironet access points (APs) are affected by a critical vulnerability that can be exploited by a remote attacker to gain unauthorized access to devices.
Chinese telecom company Huawei on Tuesday criticized the Estonian government and media for spreading what it says are “arbitrary and unfounded” allegations about cybersecurity risks related to the company’s mobile phones.
Germany released draft security guidelines on Tuesday for next generation wireless networks that stopped short of banning Huawei, as the U.S. warned again it would reconsider intelligence sharing with allies that use the Chinese company’s equipment.
Palo Alto Networks’ security researchers have identified what appears to be the first crypto-jacking worm that spreads using Docker containers.
Oracle this week announced the release of its last Critical Patch Update of 2019, which includes a total of 219 new security fixes across various product families.
Chinese tech giant Huawei said on Wednesday that its revenue for the first nine months of the year grew by almost a quarter despite a US campaign to isolate the company globally.Huawei's revenues jumped 24.4 percent on-year to 610.8 billion yuan ($86.2 billion) and its profit margin increased 8.7 percent, it announced.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
Join SecurityWeek today for a virtual summit exploring the strategies and tools organizations need to discover, prioritize, and defend their expanding attack surfaces.
Microsoft fixed vulnerabilities across Azure and AI-branded products, with privilege escalation flaws accounting for the majority.

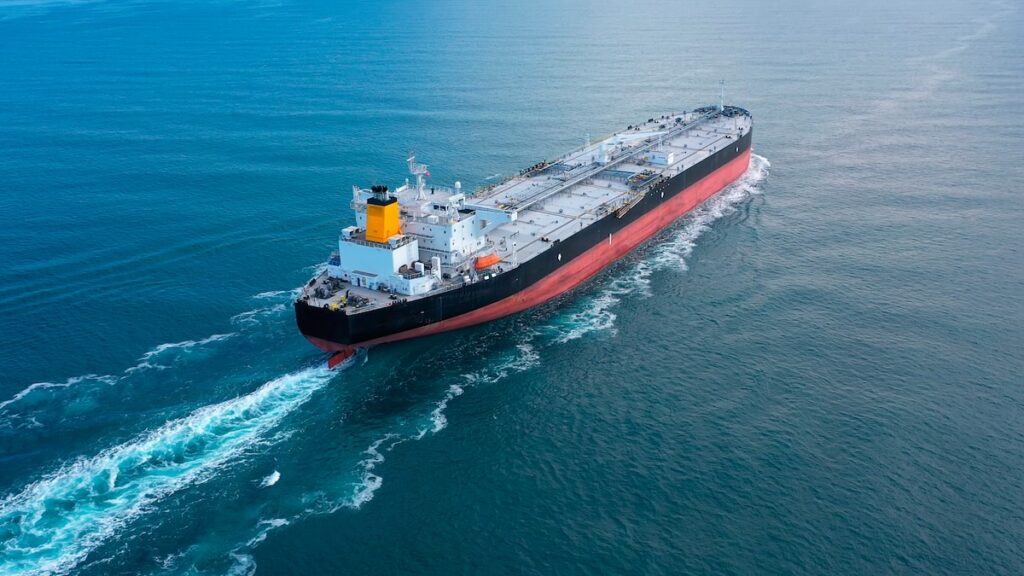
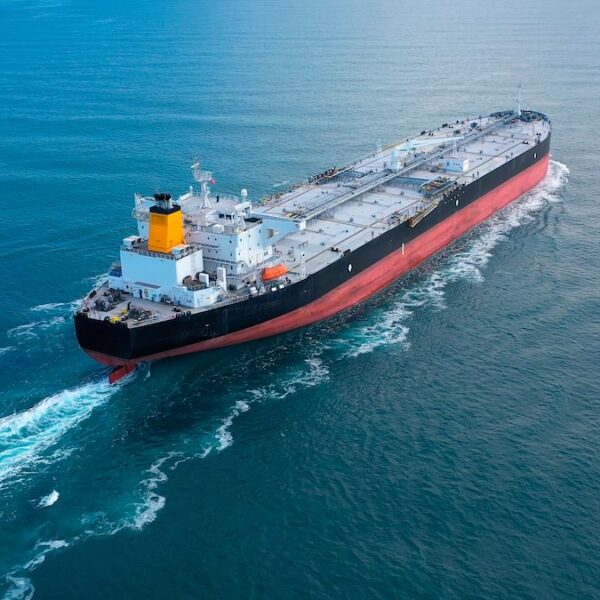
The Coast Guard confirmed evidence of malicious cyber activity on the VL Prosperity, but has not attributed the attack to Iran.