
Security researchers from Secureworks have analyzed several tools used by the Hexane threat actor in attack campaigns against industrial organizations over the past several months.

Hi, what are you looking for?

Security researchers from Secureworks have analyzed several tools used by the Hexane threat actor in attack campaigns against industrial organizations over the past several months.
Researchers at SafeBreach discovered that Check Point’s Endpoint Security product is affected by a DLL hijacking vulnerability that can be exploited for privilege escalation and other purposes.
Cybersecurity firm Avast and French police have neutralized the Retadup malware on over 850,000 computers after taking control of its command and control (C&C) server.
Australia announced Wednesday that it has formed a task force to crack down on attempts by foreign governments to meddle in Australian universities.
In 2013, a Faronics/Ponemon study found that lack of budget and poor security capability skills were the primary causes behind the generally poor state of cybersecurity in small and medium-sized businesses (SMBs). But, said Dmitry Shesterin, Faronics' VP of product management at the time, "the main reason I see," suggested Shesterin, "genuinely and honestly, they do not care -- they concentrate on business."
California-based cybersecurity firm Imperva revealed on Tuesday that it recently learned of a security incident affecting some customers of its Cloud Web Application Firewall (WAF) product, formerly known as Incapsula.
The threat actor behind the infamous Dridex and Locky malware families has updated tactics and expanded its target list in recent campaigns, Trend Micro reports.
The Libra Association, the organization in charge of Facebook’s Libra cryptocurrency, has launched a public bug bounty program with rewards of up to $10,000.
On the second day of its 2019 VMworld conference, VMware unveiled a series of new and enhanced network and security capabilities for the company’s Virtual Cloud Network offering.
Data collected by Kaspersky shows that many businesses are still using Windows 7, for which Microsoft plans on ending extended support in just a few months from now.
Apple this week released patches that address a recently re-introduced vulnerability that allows hackers to jailbreak devices.
Microsoft will be providing some of its customers with one year of free Windows 7 Extended Security Updates (ESU) after January 2020, when extended support for the platform officially ends.
The open source machine emulator QEMU is affected by a vulnerability that can lead to a denial-of-service (DoS) condition or arbitrary code execution, but developers say users should not be too concerned about its impact.
Two United States senators have sent a letter to the National Highway Traffic Safety Administration (NHTSA) to inquire about cyber-risks associated with connected vehicles.
A researcher says he has received $10,000 from Facebook after finding another critical vulnerability that could have been exploited to hack Instagram accounts.
Web hosting provider Hostinger reset all customer passwords over the weekend, after learning that an attacker gained unauthorized access to one of its internal systems.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
Join SecurityWeek today for a virtual summit exploring the strategies and tools organizations need to discover, prioritize, and defend their expanding attack surfaces.
Microsoft fixed vulnerabilities across Azure and AI-branded products, with privilege escalation flaws accounting for the majority.

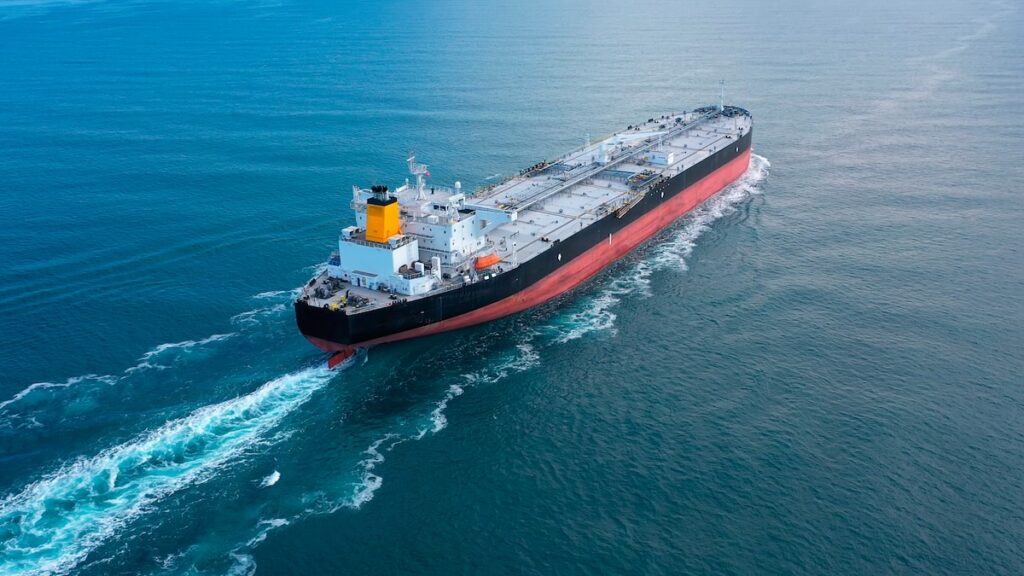
The Coast Guard confirmed evidence of malicious cyber activity on the VL Prosperity, but has not attributed the attack to Iran.