
Critical vulnerabilities discovered by researchers in Dataprobe’s iBoot power distribution unit (PDU) can allow malicious actors to remotely hack the product and shut down connected devices, potentially causing disruption within the targeted organization.
The vulnerabilities affecting the iBoot-PDU product were identified by researchers at industrial cybersecurity firm Claroty, who found a total of seven issues, including ones allowing a remote, unauthenticated attacker to execute arbitrary code.
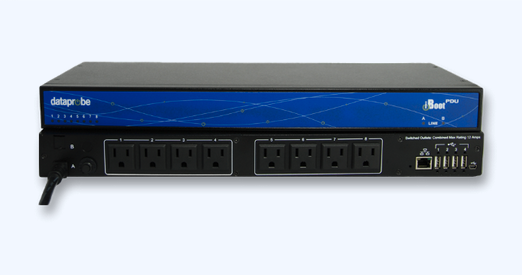 The impacted PDU provides a web interface and a cloud platform for configuring the product and controlling each individual outlet for remote power management.
A 2021 report from Censys showed that there were more than 2,000 PDUs directly exposed to the internet and nearly one-third of them were iBoot PDUs.
In addition to showing that hackers could exploit these internet-exposed devices, the Claroty researchers showed that attackers could also reach devices that are not directly exposed to the web, through the cloud-based platform that provides access to the device’s management page.
Using this cloud platform enables customers to access their devices from the web without directly exposing them to the internet — this allows users to keep the devices behind a firewall or network address translation (NAT) router.
However, the vulnerabilities found by Claroty can be exploited to bypass NAT and firewalls and achieve arbitrary code execution, enabling the attacker to cut off power to all the devices controlled by the PDU. An attacker can also obtain credentials required to move laterally within the compromised network.
The seven vulnerabilities have been assigned the CVE identifiers CVE-2022-3183 through CVE-2022-3189. The issues include OS command injection, path traversal, sensitive information exposure, improper access control, improper and incorrect authorization, and server-side request forgery (SSRF).
Claroty has published a blog post describing the more serious vulnerabilities.
The US Cybersecurity and Infrastructure Security Agency (CISA) has also released an advisory to inform organizations about these vulnerabilities. The agency said the impacted product has been deployed in multiple countries and industries, including in the critical manufacturing sector.
The vendor has patched the vulnerability with the release of firmware version 1.42.06162022. Users have been advised to update the firmware and Dataprobe also recommends disabling the Simple Network Management Protocol (SNMP) if it’s not used.
Related: Serious Vulnerabilities Found in Schneider Electric Power Meters
Related: Several Vulnerabilities Found in GE Power Meter Software
Related: Vulnerabilities in Eaton Product Can Allow Hackers to Disrupt Power Supply







You must be logged in to post a comment Login