
Hundreds of Tesla Powerwall Backup Gateways may have been exposed to remote hacker attacks from the internet, but Tesla says it has taken steps to reduce risks.
Tesla Powerwall is an energy storage product for homes that uses a battery to store power from solar panels or the grid, ensuring that users continue to have power even during an outage. The Backup Gateway component of the product is designed to provide energy management and monitoring and it’s responsible for controlling the connection to the power grid, detecting outages, and switching to backup power.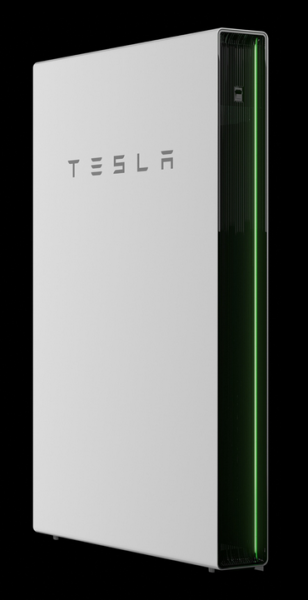
In the past, at least two research groups analyzed the product, including various undocumented API calls to the Backup Gateway and potential vulnerabilities. Members of the veteran security research group The Hacker’s Choice revealed earlier this year that a remote attacker could cause damage due to the fact that the Gateway, which is often connected to the internet via Wi-Fi, had an improperly protected management interface.
An attacker who gained access to the management interface could have taken control of the process for charging the battery from the power grid and dumping the battery’s charge back into the grid. By forcing the battery to charge from the grid at times of day when power is more expensive and unloading the charge when electricity is cheaper, the attacker could have caused financial damage.
Researchers also warned at the time that by quickly switching between charging and dumping, an attacker could have caused damage to the Powerwall device and possibly even the electrical substation.
Researchers at cybersecurity firm Rapid7 have also analyzed the Backup Gateway and on Tuesday they reported observing a total of 379 installations since January 2020. This number mostly consists of residential products, but experts believe some of them are commercial-grade Tesla Powerpack systems, which are significantly larger than the residential batteries.
Rapid7 said 160 of the Gateway devices were located in the United States, with significant numbers located in Italy and France.
The company explained that exposed devices are easy to find on the web due to the fact that the Backup Gateway exposes a web server on HTTPS port 443. Once a device has been identified, accessing it may not be difficult due to the use of weak default credentials. Specifically, the password for the first login is the last five characters of the Gateway serial number, which can be obtained from various sources, including a label on the device, the mobile app, and partially from the name of the Wi-Fi access point broadcasted by the gateway (this makes brute-force attacks easier to conduct).
“I am fairly alarmed at the number of these devices on the internet,” explained Derek Abdine, former director of Rapid7 Labs and current CTO of internet search engine Censys. “The numbers may be relatively low, but given the devices are massive batteries that deal in high voltage and current, malicious manipulation could lead to potential physical harms. It is also possible to pinpoint these even if they aren’t internet connected through weakly configured home routers, and pivot from those routers into the LAN to control them that way.”
Rapid7 disclosed its findings to Tesla before publishing its blog post and the car maker said it had already taken some steps to make authentication more secure, and it plans on rolling out more security features in the future. SecurityWeek has reached out to Tesla for comment, but it has yet to hear back.
Related: Tesla Breach: Malicious Insider Revenge or Whistleblowing?
Related: Russian Pleads Not Guilty in Foiled Tesla Ransomware Plot







You must be logged in to post a comment Login