
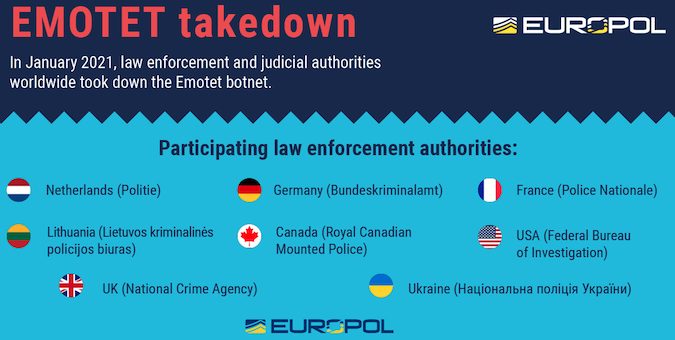
Authorities have managed to disrupt the infrastructure of the Emotet botnet, as part of an international effort of law enforcement agencies across Europe and North America.
One of the most prevalent botnets over the past decade, Emotet first emerged in 2014 as a banking Trojan, but evolved into a malware downloader used by many cybercriminals looking to spread their malicious payloads.
Emotet has become, as Europol described it, “a primary door opener for computer systems on a global scale,” as its operators were selling access to infected computers to cybercrime groups that engaged in activities such as data theft or extortion.
Using automation, Emotet’s operators were spreading the Trojan via malicious email attachments, leveraging a broad range of lures to trick victims into opening them. Some of the emails were masquerading as invoices and shipping notices, while others featured COVID-19 themes.
Malicious documents attached to the emails or linked to in the message would ask the user to enable macros, which allowed malicious code to run in the background and install Emotet.
Emotet then acted as a loader, as its operators allowed other cybercriminals to rent the botnet to deploy their own malware, including banking Trojans, ransomware, and other malicious applications. The TrickBot Trojan and Ryuk ransomware are known to have been distributed via Emotet.
Emotet’s infrastructure, which included several hundreds of servers worldwide, allowed operators to manage infected computers, spread to new machines, offer services to other criminal groups, and improve the network’s resilience.
In order to take down the botnet, law enforcement and judicial authorities took control of the infrastructure “from the inside,” and infected machines are now redirected to this law enforcement-controlled infrastructure.
Authorities in the Netherlands, France, Germany, the United States, Canada, the United Kingdom, Lithuania, and Ukraine collaborated in this operation, coordinated by Europol and Eurojust.
The Dutch National Police’s investigation into Emotet has led to the discovery of a database of email addresses, usernames, and passwords stolen by the malware. Users can now check if their email address is included in the database.
“As part of the global remediation strategy, in order to initiate the notification of those affected and the cleaning up of the systems, information was distributed worldwide via the network of so-called Computer Emergency Response Teams (CERTs),” Europol notes.
A video of a house search performed as part of the operation, which the National Police of Ukraine published on YouTube, shows authorities seizing hard drives, computers, and other equipment, along with large amounts of money and what appear to be gold bars, which clearly shows that Emotet was a highly profitable cybercriminal enterprise.
Related: CISA Warns of Emotet Trojan Targeting State, Local Governments
Related: Emotet Resumes Activity After Five Months of Silence
Related: ‘Vaccine’ Kept Emotet Infections Away for Six Months







You must be logged in to post a comment Login