
A critical remote code execution vulnerability discovered by an IBM X-Force researcher allows an unauthenticated attacker to take complete control of some TP-Link Wi-Fi extenders. Firmware updates that should patch the flaw have been made available by the vendor.
While analyzing some TP-Link routers, IBM X-Force researcher Grzegorz Wypych came across a potentially serious vulnerability in the TP-Link RE365 Wi-Fi extender running firmware version 1.0.2, build 20180213. Following its own analysis, the vendor determined that the security hole also impacts RE650, RE350 and RE500 devices.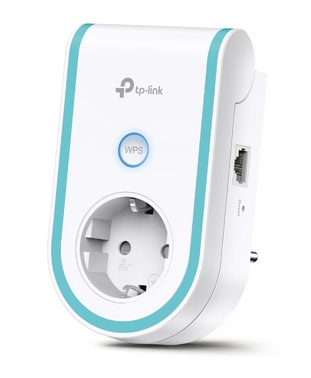
Wi-Fi extenders are designed to forward signal captured from a wireless router in order to extend its range.
The issue affecting TP-Link extenders, tracked as CVE-2019-7406, can be exploited by a remote and unauthenticated attacker via specially crafted user agent fields in HTTP headers. Since all processes on the impacted extenders run with root privileges, an attacker can execute arbitrary shell commands with elevated permissions and take complete control of the device.
“This vulnerability can […] affect a variety of end users, from home users to corporate users, and enable an attacker to send any request to the extender. The sort of impact that can result from such unauthenticated access includes, for example, requesting the device to browse to a botnet command-and-control (C&C) server or an infection zone,” Wypych explained in a blog post. “The thought of a Mirai infection on internet of things (IoT) devices is, of course, one of the first things that comes to mind, where automated scripts could potentially run as root on this type of device if the vulnerability is exploited.”
TP-Link has released firmware updates for each of the affected models in an effort to address the vulnerability. No other devices appear to be impacted.
Related: 0-Day in TP-Link SR20 Routers Allows Command Execution
Related: Flaws Affecting Top-Selling Netgear Routers Disclosed
Related: TP-Link Patches Remote Code Execution Flaws in SOHO Router






