
A researcher has disclosed the details and created Metasploit modules for Cisco UCS vulnerabilities that can be exploited to take complete control of affected systems.
Cisco last week informed customers that it released patches for 17 critical and high-severity flaws affecting some of the company’s Unified Computing System (UCS) products, including Integrated Management Controller (IMC), UCS Director, and UCS Director Express for Big Data.
Many of the security holes were found by Cisco itself, but some have been reported to the networking giant by researcher Pedro Ribeiro.
Ribeiro announced on Wednesday that he has released the details of three vulnerabilities that can be exploited by malicious actors to gain complete control over affected systems.
One of the flaws, tracked as CVE-2019-1935 and classified as critical, can allow a remote attacker to log in to the command-line interface (CLI) of a vulnerable system using the SCP user account (scpuser), which has default credentials.
According to Ribeiro, the SCP user is designed for diagnostics and tech support operations and it should normally not provide access to the GUI or shelladmin. However, the researcher found that this user can log in via SSH with the default password if it hasn’t been changed by the administrator.
Another vulnerability identified by Ribeiro is CVE-2019-1936, a high-severity issue that allows an authenticated attacker to execute arbitrary commands on the underlying Linux shell with root permissions.
While this vulnerability requires authentication, that can be achieved using another critical vulnerability discovered by the researcher. CVE-2019-1937 allows a remote and unauthenticated attacker to bypass authentication by acquiring a valid session token with admin privileges. An attacker can obtain this token by sending a series of malicious requests to the targeted device.
Ribeiro says CVE-2019-1936 and CVE-2019-1937 can be chained by a remote attacker with no privileges on the targeted system to execute code as root and take complete control of the affected product.
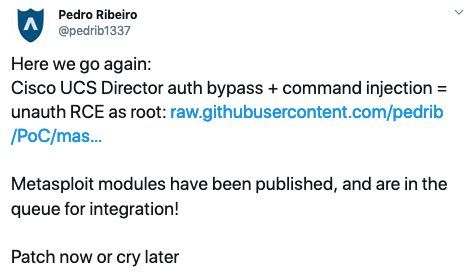
Ribeiro has developed two Metasploit modules that are in the process of being integrated. One targets the default SSH password, while the other combines the authentication bypass and command injection vulnerabilities.
Related: Cisco Improperly Patched Exploited Router Vulnerabilities
Related: Cisco Warns of Zero-Day Vulnerability in Security Appliances
Related: Cisco ASA Flaw Exploited in DoS Attacks
Related: Cisco Aware of Attacks Exploiting Critical Firewall Flaw







You must be logged in to post a comment Login