The US Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) has confirmed suffering a cybersecurity incident after the Qilin ransomware group claimed to have targeted the agency.
In a statement on its website, ATF said the incident affected a standalone system, which was disconnected after the intrusion was discovered.
“The impacted system operates separately from the ATF enterprise network, and there is no indication that the incident has affected the ATF enterprise network, the ATF eForms system, or any other ATF system,” ATF said, adding, “The incident has not impacted ATF’s ability to perform its missions.”
An investigation is being conducted in coordination with the Justice Department.
“Senior Department officials have designated the event a ‘major incident’ under applicable federal guidelines, and required notifications have been completed,” ATF noted.
The Qilin ransomware group added ATF to its leak website on August 26, but it has not made any specific claims about the breach.
The hackers often post screenshots to demonstrate that certain types of documents have been stolen from victims, but that has yet to happen in ATF’s case.

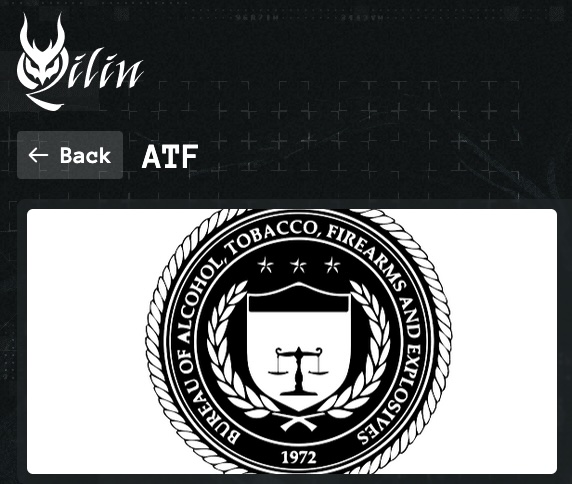
Qilin’s post also does not specify when any stolen files might be leaked; some victim announcements include a timer indicating when files will be published.
Active since at least 2022 — initially under the name Agenda — Qilin operates on a double-extortion model, encrypting files and exfiltrating sensitive information from victims’ systems.
Qilin made headlines recently after it exploited a Check Point VPN zero-day vulnerability in its attacks.
The cybercrime group has listed more than 2,000 victims on its leak website to date, and the actual number is likely much higher, given that many pay a ransom and are not named.
Related: Cl0p Ransomware Group Names Over 40 Victims of PTC Windchill Campaign
Related: Sensitive Information Exposed in Nutex Health Data Breach
Related: ReliaQuest Confirms ShinyHunters Hack, but Says Impact Was Limited