
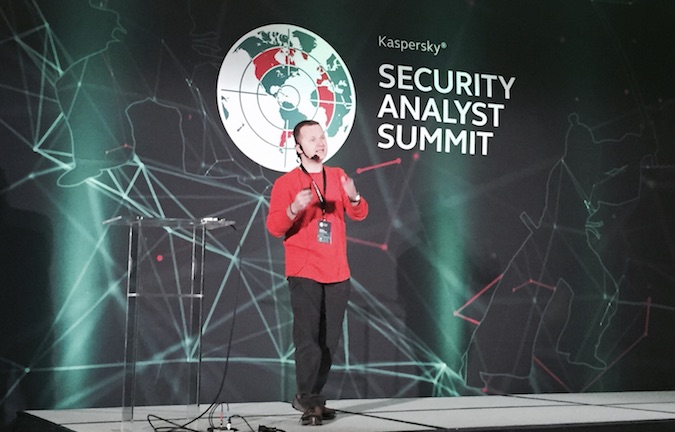
Kaspersky Lab security expert Dmitry Bestuzhev presents research on “Desert Falcons” at the Kaspersky Lab Security Analyst Summit on Feb. 17.
CANCUN, Mexico – Kaspersky Lab Security Analyst Summit – Threat actors with Arabic roots are targeting multiple high profile organizations and individuals from Middle Eastern countries, according to a new report from Kaspersky Lab.
The attack group, dubbed “Desert Falcons” by the security firm, appears to be the first known Arabic cyber-espionage group to develop and run full-scale cyber-espionage operations, researchers said.
Details of the campaign, which has been active for at least two years, were unveiled at Kaspersky Lab’s Security Analyst Summit in Cancun, Mexico on Tuesday.
According to Kaspersky researchers, the peak of their activity occurred at the beginning of 2015, and so far, the attackers have been able to steal more than one million files from more than 3,000 victims in over 50 countries.
Kaspersky Lab began its investigation of the group in August 2014, and has so far been able to identify a total of more than 100 malware samples used by the group in their attacks.
While the vast majority of targets based in Egypt, Palestine, Israel and Jordan, victims were also found in Qatar, KSA, UAE, Algeria, Lebanon, Norway, Turkey, Sweden, France, the United States, Russia and other countries, Kaspersky said.
Targeted victims include Military and Government organizations, media outlets, research and education institutions, energy and utilities providers, activists and political leaders; physical security companies; and other targets holding geopolitical information.
According to Kaspersky Lab, attackers have primarily used malware-laden spear phishing e-mails, along with social engineering techniques through social networking sites and chat messages to infect victims.
After infecting the system of a victim, the attackers used one of two different Backdoors: the main Desert Falcons’ Trojan or the DHS Backdoor, both which appear to have been developed from scratch and are in continuous development, Kaspersky said.
Malware tools used by the group, were made from scratch and target both Windows PCs and Android-based devices. The tools used have full Backdoor functionality, including the ability to take screenshots, log keystrokes, upload/download files, collect information about all Word and Excel files on a victim’s Hard Disk or connected USB devices, steal passwords stored in the system registry and make audio recordings.
The Android malware appears to be a backdoor capable of stealing mobile calls and SMS logs, the firm said.
“The individuals behind this threat actor are highly determined, active and with good technical, political and cultural insight. Using only phishing emails, social engineering and homemade tools and backdoors, the Desert Falcons were able to infect hundreds of sensitive and important victims in the Middle East region through their computer systems or mobile devices, and exfiltrate sensitive data,” said Kaspersky Lab security expert Dmitry Bestuzhev.
“We expect this operation to carry on developing more Trojans and using more advanced techniques. With enough funding, they might be able to acquire or develop exploits that would increase the efficiency of their attacks,” he said.






You must be logged in to post a comment Login