
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Application Security

Apple Ships Emergency Patches for ‘Actively Exploited’ macOS, iOS Flaws

Apple’s security response team on Thursday released emergency patches to cover a pair of “actively exploited” vulnerabilities affecting macOS, iOS and iPadOS devices.

Apple’s security response team on Thursday released emergency patches to cover a pair of “actively exploited” vulnerabilities affecting macOS, iOS and iPadOS devices.

Apple confirmed the two security defects — CVE-2022-22675 and CVE-2022-22674 — in all its major operating systems and warned that remote code execution attacks may already be underway.

One of the two vulnerabilities, described as an out-of-bounds memory corruption issue in AppleAVD, affects both iOS and macOS devices.
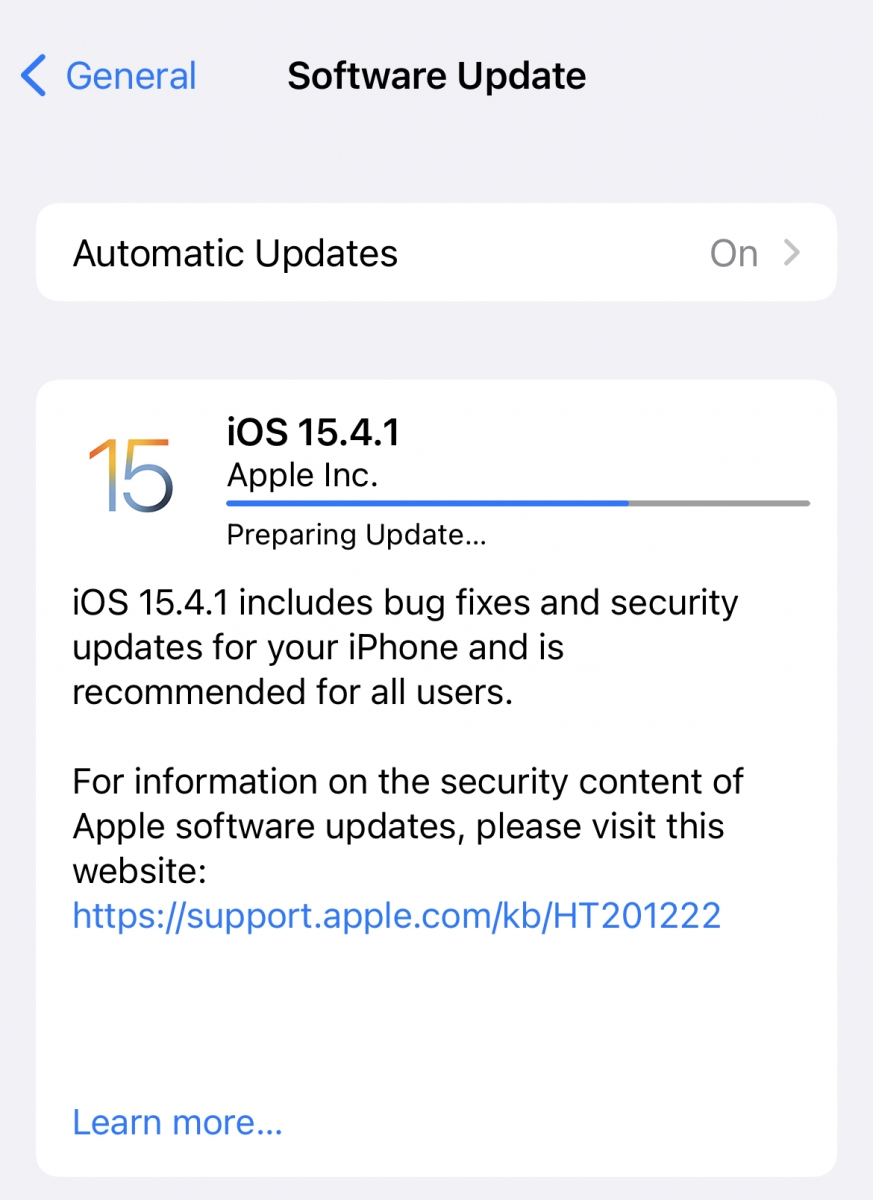
iOS update 15.4.1 fixes CVE-2022-22675 and CVE-2022-22674 “An application may be able to execute arbitrary code with kernel privileges. Apple is aware of a report that this issue may have been actively exploited,” the Cupertino, California company said in a barebones advisory.

[ READ: New Modem Wiper Malware May be Connected to Viasat Hack ]

Apple released iOS 15.4.1 and iPadOS 15.4.1 and urged users to apply the updates to reduce exposure to risk.

The company separately released macOS Monterey 12.3.1 with fixes for the AppleAVD bug and a second flaw in the Intel Graphics Driver, warning that a successful attacker can read kernel memory.

Advertisement. Scroll to continue reading.

“An out-of-bounds read issue may lead to the disclosure of kernel memory and was addressed with improved input validation. Apple is aware of a report that this issue may have been actively exploited,” the company said.

As is customary, the company did not provide any details or indicators or compromise to help its users detect signs of malicious activity.

According to SecurityWeek tracking data, there have been at least 13 documented zero-day attacks so far this year.    

Related: North Korea Gov Hackers Caught Sharing Chrome Zero-Day

Related: The Chaos (and Cost) of the Lapsus$ Hacking Carnage

Related: Apple Patch Day: Gaping Security Holes in iOS, macOS, iPadOS
Written By

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. He is a security community engagement expert who has built programs at major global brands, including Intel Corp., Bishop Fox and GReAT. Ryan is a founding-director of the Security Tinkerers non-profit, an advisor to early-stage entrepreneurs, and a regular speaker at security conferences around the world.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Trending

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Learn how to address potential risks and not restrict AI adoption in your organization. See what a centralized AI gateway is and how it works in practice.

Register

Join as we decipher the world of zero trust and share war stories on securing an organization by eliminating implicit trust and continuously validating every stage of a digital interaction.

Register

People on the Move

David Cass has joined Grayscale Investments as Chief Risk Officer. He joins the crypto investment funds firm from Keyrock, where he served as Chief Information Security Officer.

Thomas Dager has been appointed Vice President and Chief Information Security Officer at The Goodyear Tire & Rubber Company.

Alex Stamos has become Chief Information Security Officer at Cognition.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





