
Updates released by Apple on Monday for iOS, macOS, tvOS and watchOS patch a flaw that causes applications to crash when rendering specific strings of Indian characters.
Someone noticed recently that displaying a string written in India’s Telugu language (జ్ఞా) caused many apps on iOS and macOS to crash. The list of impacted apps includes Twitter, Firefox, Chrome, Safari, WhatsApp, Mail, Thunderbird, Instagram, Slack and others.
Apple became aware of the issue after news of the bug started to spread on social media networks and trolls and pranksters started exploiting it. One individual apparently showed how he could crash the Uber app on drivers’ phones by setting his name to the problematic string and requesting a ride.
SecurityWeek can confirm that conducting a search for the string in any web browser on macOS causes the applications to immediately crash. Attempting to send or receive an email using Mail or Thunderbird has the same effect.
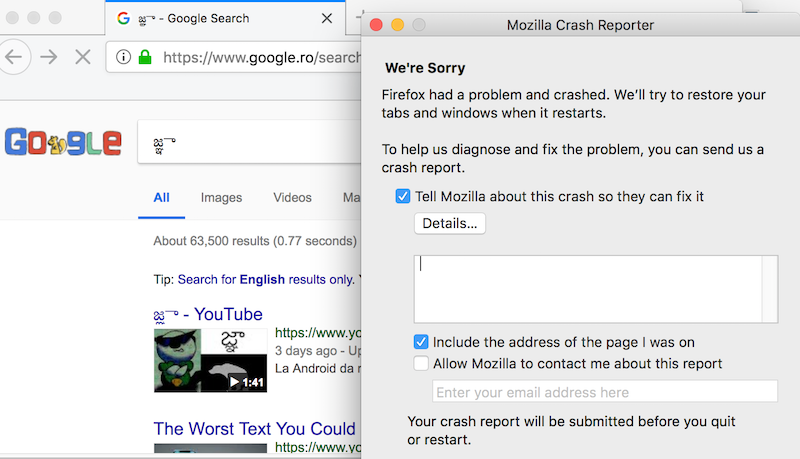
While initially only a certain Telugu string appeared to work, some later noticed that a specific string using characters of India’s Bengali language also caused apps on iOS and macOS to crash. There are several theories on what may be causing the crash, including from Mozilla research engineer Manish Goregaokar and Philippe Verdy of the Unicode Consortium.
Apple tracks the vulnerability as CVE-2018-4124 and describes it as a heap corruption triggered when processing a maliciously crafted string. “A memory corruption issue was addressed through improved input validation,” Apple said.
The company patched the flaw on Monday with the release of macOS High Sierra 10.13.3 Supplemental Update, iOS 11.2.6, watchOS 4.2.3 and tvOS 11.2.6. watchOS and tvOS are affected due to the fact that they are based on iOS. The latest operating system updates don’t fix any other vulnerabilities.
Related: Apple Working on Patch for New Year’s Eve macOS Flaw
Related: Apple Patches Critical Root Access Flaw in macOS
Related: Apple Patches Meltdown Flaw in Older Versions of macOS







You must be logged in to post a comment Login