Electronics giant Acer has confirmed getting hacked after a hacker offered to sell 160 Gb of files allegedly stolen from the company’s systems.
“We have recently detected an incident of unauthorized access to one of our document servers for repair technicians. While our investigation is ongoing, there is currently no indication that any consumer data was stored on that server,” Acer told SecurityWeek in an emailed statement.
Acer issued the statement after a hacker announced on a popular cybercrime forum that he is selling more than 2,800 files totaling 160 Gb for an unspecified amount of Monero cryptocurrency.
The cybercriminal claims the files include confidential slides, staff manuals, confidential product documentation, binary files, information on backend infrastructure, disk images, replacement digital product keys, and BIOS-related information.

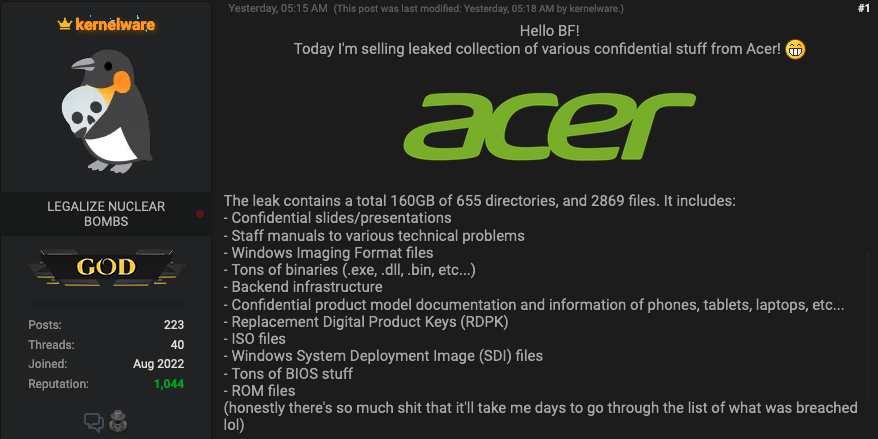
The hacker, who has a good reputation on the forum where the data was offered for sale, claimed the data was stolen in mid-February.
This is not the first time Acer has confirmed a data breach. In October 2021, the tech giant admitted that servers in India and Taiwan were hacked after a group claimed to have stolen more than 60 Gb of data from the company’s systems.
Related: 25k Nissan Customers Affected by Data Breach at Third-Party Software Developer
Related: Atlassian Investigating Security Breach After Hackers Leak Data
Related: 20 Million Users Impacted by Data Breach at Instant Checkmate, TruthFinder