
Oil and gas flow computers and remote controllers made by Swiss industrial technology firm ABB are affected by a serious vulnerability that could allow hackers to cause disruptions and prevent utilities from billing their customers, according to industrial cybersecurity firm Claroty.
Utilities rely on flow computers to calculate oil and gas flow rates and volume. These devices, which are often used in the electric power sector, play an important role in process safety, as well as billing.
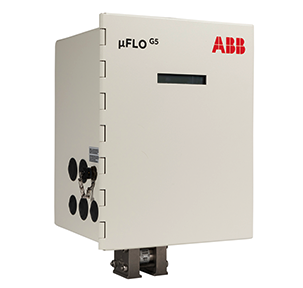 Researchers at Claroty showed how an attacker with access to a targeted flow computer can bypass authentication using a brute-force attack, and then exploit a path traversal vulnerability to read the device’s shadow password file to obtain its root account password. The same vulnerability can be used to modify the SSH configuration file to enable password authentication and allow the attacker to access the device with root privileges.
This entire exploit chain can allow a remote, unauthenticated attacker to execute arbitrary code with root privileges. The hacker can take complete control of the device and disrupt its ability to measure oil and gas flow, which can prevent the victim from billing customers.
One perfect example of the importance of billing systems is provided by the 2021 Colonial Pipeline ransomware attack, where the company reportedly halted operations not because the hackers hit operational technology (OT) systems, but because its billing system was compromised.
Claroty reported its findings to ABB, which announced the release of firmware patches for affected products in July. The path traversal vulnerability is tracked as CVE-2022-0902 and it has been assigned a ‘high severity’ rating.
ABB has determined that its XFC G5 and uFLO G5 flow computers, RMC-100, XRC G5, and XIO remote controllers, as well as the Totalflow Universal Data Controller (UDC) are impacted. The vendor said in its July advisory that it was not aware of any attacks exploiting the vulnerability.
Claroty has published a blog post detailing its research, as well as a video showing how an attacker could hack a device.
Related: iBoot Power Distribution Unit Flaws Allow Hackers to Remotely Shut Down Devices
Related: New Vulnerabilities Allow Stuxnet-Style Attacks Against Rockwell PLCs
Related: Moxa MXview Vulnerabilities Expose Industrial Networks to Attacks







You must be logged in to post a comment Login