
The NATO Cooperative Cyber Defence Centre of Excellence (CCDCOE) in Estonia last week hosted the 2023 edition of the annual Locked Shields cyber defense exercise.
Compared to last year’s event, when roughly 2,000 participants represented 32 countries, the 2023 Locked Shields exercise had 3,000 participants from 38 countries.
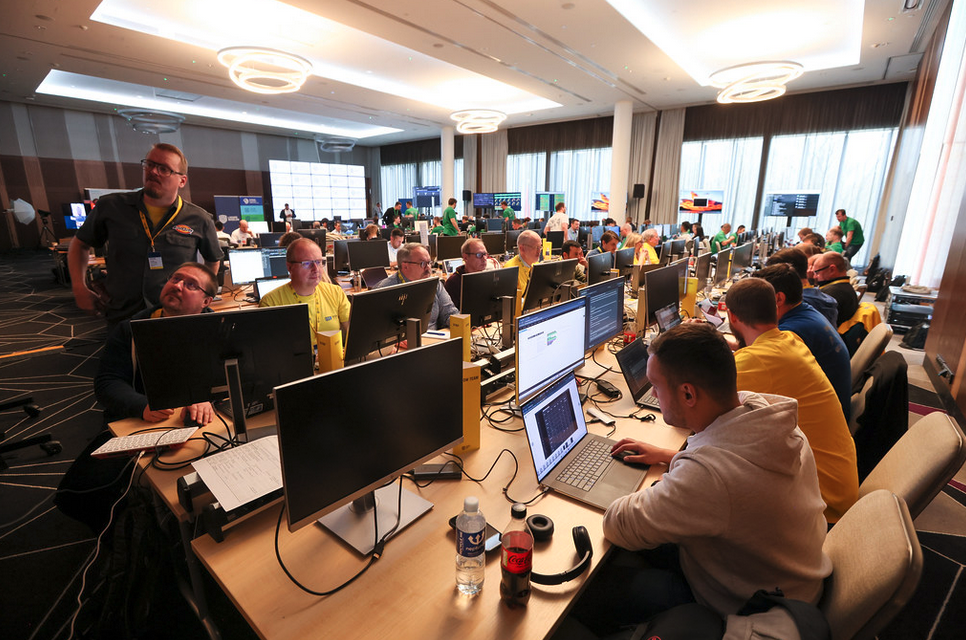
The fact that the number of participants has been increasing is likely — at least partially — the result of Russia’s war against Ukraine, which has also had a significant cyber component that has underscored the importance of good cyber resilience and response capabilities.
Organized at the CCDCOE for more than a decade, the exercise tests participants’ ability to defend systems against real-time attacks, handle incident reporting, and solve challenges related to forensics, the media, and legal issues.
At Locked Shields, attacking Red Teams compete against defending Blue Teams, with the Blue Team being tasked to defend a made-up country’s information systems and critical infrastructure, including energy and banking systems, from large-scale attacks.
“This past year has shown us how important strength in cyber defense is,” said Estonian Minister of Defence Hanno Pevkur. “Cyber warfare may not be as visible as kinetic warfare, but it is integrated into wartime activities. Ukraine has strong digital competences, and that has meant that their state can keep delivering essential digital services even in wartime. Cyber competence grows through investments, but not only monetary ones – exercises like these, where allies with shared values also exchange know-how and train together, are key to continued resilience.”
NATO countries are often targeted by state-sponsored cyberespionage groups and governments are aware that there is always the risk that hackers, including less sophisticated threat actors, could try to launch disruptive or destructive attacks on critical infrastructure.
Related: NATO Seeks Contractors to Test Security of Web Assets
Related: NATO’s Team in Albania to Help on Iran-Alleged Cyberattack
Related: China Not Happy With South Korea Joining NATO Cyber Defense Center






