
Germany-based industrial solutions provider Weidmueller on Wednesday informed customers that it has patched a dozen vulnerabilities affecting some of its industrial WLAN devices.
Weidmueller provides a wide range of connectivity, electronics, automation, assembly and workplace products to organizations worldwide, particularly in the machinery, energy, device manufacturing, transportation, process, and building infrastructure sectors.
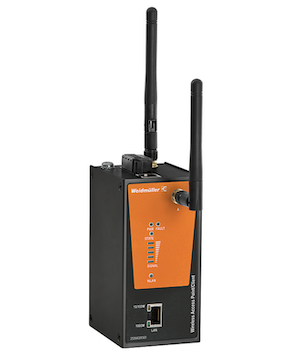 In security advisories published on Wednesday by Weidmueller and Germany’s CERT@VDE, which coordinates cybersecurity issues related to industrial automation, organizations were informed about 12 types of vulnerabilities discovered by the vendor in its industrial WLAN devices.
The security holes impact wireless access point/bridge/client devices running firmware versions prior to 1.16.21 (build 21010513) or 1.11.13 (build 21010513). Weidmüller has advised customers to install the latest firmware to secure their devices.
The vulnerabilities, tracked with the CVE identifiers CVE-2021-33528 through CVE-2021-33539, can be exploited for privilege escalation, decryption of traffic, arbitrary code/command execution, denial-of-service (DoS) attacks, and authentication bypass.
Exploitation of many of the flaws requires authentication — at least with low privileges — and it’s unclear if the authentication bypass vulnerability can be chained with the other vulnerabilities. Nevertheless, Weidmuller and CERT@VDE have rated each of the issues as high severity.
Learn More About Vulnerabilities in Industrial Products at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits Virtual Event Series
Due to the fact that Weidmueller products are used all over the world, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) also released advisories for vulnerabilities in the company’s products in the past. However, CISA has yet to release an advisory for these flaws.
Related: Weidmueller Patches Critical Vulnerabilities in Industrial Switches
Related: Moxa Addresses Industrial AP Vulnerabilities Several Months After Disclosure
Related: ICS Vendors Assessing Impact of New OPC UA Vulnerabilities
Related: Critical Vulnerabilities Expose Pepperl+Fuchs Industrial Switches to Attacks






