
Switches used by organizations around the world are affected by critical vulnerabilities that could allow malicious actors to gain remote access to enterprise networks and steal valuable data, according to enterprise device security company Armis.
Earlier this year, Armis warned that uninterruptible power supply (UPS) products made by Schneider Electric subsidiary APC are affected by critical vulnerabilities that can be exploited to remotely hack and damage devices.
The root cause of the UPS vulnerabilities, named TLStorm by Armis, was related to the implementation of Mocana’s popular TLS library NanoSSL. Further analysis showed that other vendors also introduced similar vulnerabilities in their products due to misuse of the same TLS library.
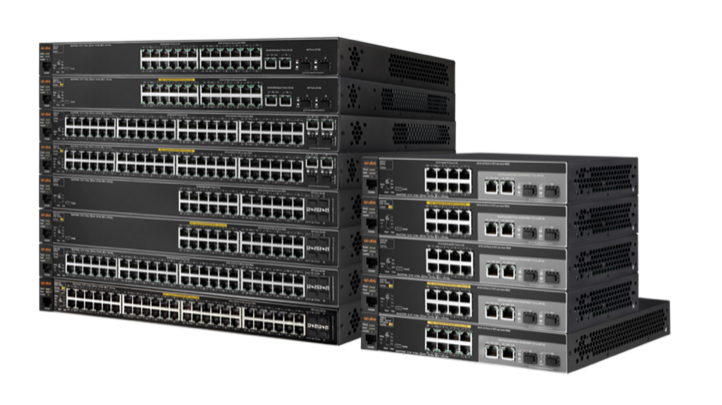 Armis researchers discovered a new round of vulnerabilities, which they have dubbed TLStorm 2.0, in switches made by Extreme Networks-owned Avaya and HPE subsidiary Aruba.
Aruba switches are affected by two types of critical vulnerabilities tracked as CVE-2022-23677 and CVE-2022-23676, while Avaya devices are affected by CVE-2022-29860 and CVE-2022-29861. Each of these vulnerabilities can allow remote code execution (RCE) on the impacted device.
Another RCE vulnerability affecting Avaya devices has not been assigned a CVE identifier due to the fact that it impacts discontinued products, but Armis warned that the vulnerable devices are still in use.
The cybersecurity company has described several theoretical attack scenarios involving these vulnerabilities. One of them is related to captive portals, the web page that users see when trying to access a corporate network or the internet from an airport or a hotel.
An attacker could exploit the TLStorm 2.0 vulnerabilities to abuse a captive portal and achieve arbitrary code execution on a switch without authentication. Once they have control of the switch, the attacker can disable the captive portal and freely access the protected corporate network.
Attackers could also exploit the TLStorm 2.0 flaws to take control of a core switch, which enables them to break network segmentation and move laterally on the network.
Exploitation of the vulnerabilities can give an attacker access to sensitive information stored on the targeted network, which they can exfiltrate to remote servers.
The vulnerabilities have been found to affect Avaya ethernet routing switch (ERS) series devices and seven types of switches from Aruba.
The vendors have been notified. Aruba is working on patches and Avaya has already released firmware updates for some of the impacted products. Armis says it’s not aware of any malicious attacks exploiting the vulnerabilities.
*updated to say that Aruba and Avaya are still working on patches
Related: Critical Vulnerability Can Be Exploited to Hack Schneider Electric’s Modicon PLCs
Related: Flaws in Pneumatic Tube System Can Facilitate Cyberattacks on North American Hospitals







You must be logged in to post a comment Login