The US Department of the Treasury’s Office of Foreign Assets Control (OFAC) has announced sanctions against a Chinese technology company for supporting cyberattacks against US critical infrastructure.
Based in Beijing, the sanctioned firm, Integrity Technology Group (Integrity Tech), develops and sells cybersecurity products such as network simulation, network security training, and network security competition solutions.
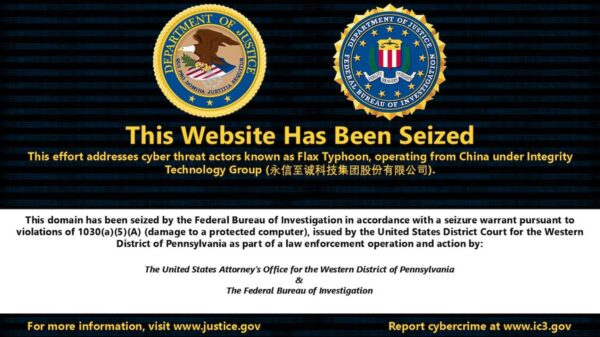
According to the US Treasury, between summer 2022 and fall 2023, Integrity Tech infrastructure was used by the Chinese state-sponsored hacking group Flax Typhoon in cyberattacks against multiple victims.
“During that time, Flax Typhoon routinely sent and received information from Integrity Tech infrastructure,” the US Treasury says.
Active since at least 2021, Flax Typhoon has hit entities in North America, Europe, Africa, and Asia, with a focus on Taiwan, exploiting known vulnerabilities to hack computers and establishing persistent access to the compromised networks.
Flax Typhoon has been observed targeting organizations within various industries, including the US critical infrastructure. Between summer 2022 and fall 2023, the threat actor used VPN and RDP solutions to access hosts associated with US and European entities.
“In summer 2023, Flax Typhoon compromised multiple servers and workstations at a California-based entity,” the US Treasury says.
In September 2024, the US government announced the disruption of Raptor Train, a Flax Typhoon-operated botnet that ensnared more than 260,000 routers, network-attached storage (NAS) devices, and IP cameras.
The botnet enabled Flax Typhoon to route traffic, launch distributed denial-of-service (DDoS) attacks, and deliver other malware, and had been used in attacks targeting military, government, higher education, telecommunications, and defense industrial base entities in the US and Taiwan.
In its description of the botnet, the US said that Integrity Tech had controlled and managed the botnet since mid-2021, using “China Unicom Beijing Province Network IP addresses”.
The same IP addresses were also used “to access other operational infrastructure employed in computer intrusion activities against US victims,” the US said.
OFAC is now designating Integrity Tech for its role in cyberattacks targeting US critical infrastructure and the potential threat posed to “national security, foreign policy, or economic health or financial stability of the United States”.
The designation results in Integrity Tech’s property located in the US being blocked and entities and individuals in the US being prohibited from engaging in certain transactions or activities with the Chinese company.
Related: US Imposes Sanctions on Russian and Iranian Groups Over Disinformation Targeting American Voters
Related: AP Sources: Chinese Hackers Targeted Phones of Trump, Vance, People Associated With Harris Campaign
Related: Huawei Has Replaced Thousands of US-Banned Parts With Chinese Versions: Founder
Related: US Revokes Visas For 1,000 Chinese Under Trump Order