Malware & Threats
Cisco Talos linked SD-WAN key-stealing malware to infrastructure overlapping Volt Typhoon’s Silent Train network, which Lumen detailed.
Hi, what are you looking for?

Cisco Talos linked SD-WAN key-stealing malware to infrastructure overlapping Volt Typhoon’s Silent Train network, which Lumen detailed.
The attackers chained PHP2Shell and Fragnesia exploits and hacked two servers of a US government-affiliated organization.

Xint says a flaw in OpenAI’s compaction process let researchers move reasoning traces between models, potentially making it cheaper to distill a rival AI.
The state-sponsored hackers targeted hundreds of organizations and gained privileged access to some environments.

The DHS said agencies should remove DeepSeek products as well as third-party products and services developed using DeepSeek from their IT systems.
Tasked with writing an application for a US defense contractor, the model made the code 19% more likely to be hackable.
At least three threat actors have been abusing Cairn for persistent access and financial theft.
Armory Castle exploited CVE-2026-102764 for initial access, deployed custom tools, and deleted logs and artifacts.
Backed by a federal court order, Microsoft and Health-ISAC seized domains powering YAM Store, CoGUI, and Iron Man.
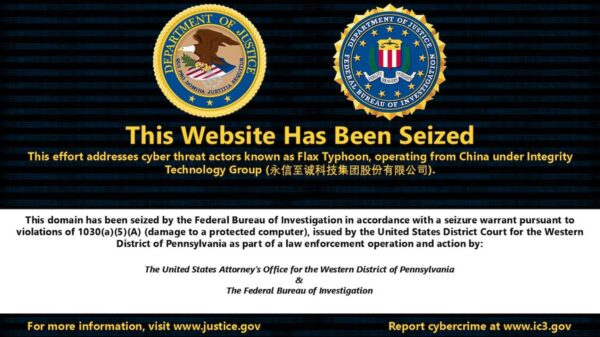
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure.
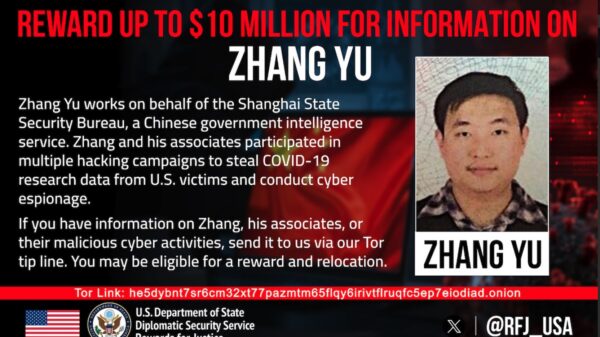
Zhang Yu was charged alongside Xu Zewei, who was extradited from Italy to the US in April 2026.

SEC Consult has published technical details on vulnerabilities mentioned in a complaint filed by several US states.
The China-based hacking group has been exploiting SharePoint vulnerabilities since July 2025.
The malware framework uses a modular architecture and a custom executable file format for long-term persistence.
The US and China agreed to set up a communication mechanism for artificial intelligence-related incidents.
China’s Ministry of Foreign Affairs responded to a question about Amodei’s essay by saying that all parties should work together on AI.
The Chinese-language input method editor for Windows can allow attackers to execute arbitrary code remotely.
Distillation is an ‘attack’ against an AI model designed to capture outputs, understand reasoning processes, and subsequently train a different model.
New research shows that country-of-origin labels can obscure an AI model’s upstream dependencies, inherited behaviors and potential security risks.
The operation focused on a group named QTFY, which offers hacking services to the Chinese government and others.


The mod_http2 race condition, CVE-2026-119618, could let unauthenticated attackers execute code on servers with HTTP/2 enabled.

Google fixed 83 flaws with a new Chrome 157 release, and Mozilla addressed 99 bugs in Firefox 160.