
The US Cybersecurity and Infrastructure Security Agency (CISA) has instructed government agencies to immediately address a vulnerability affecting Windows DNS servers.
The critical vulnerability, tracked as CVE-2020-1350 and dubbed SIGRed, was patched by Microsoft on Tuesday with its security updates for July 2020.
The flaw, which impacts Windows Server versions released in the past 17 years, allows a remote, unauthenticated attacker to run arbitrary code on affected Windows DNS servers using specially crafted requests. Since it’s wormable, it can be exploited by malware to spread without user interaction.
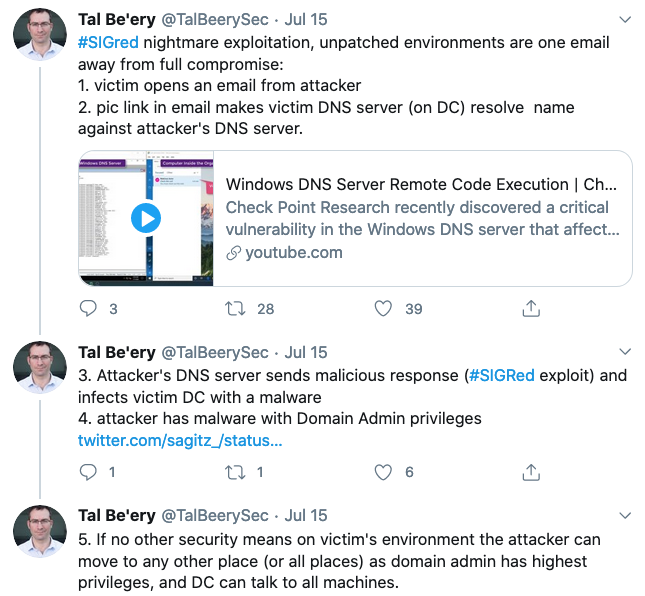
Security researcher Tal Be’ery has described a possible attack scenario involving this weakness.
While attacks exploiting SIGRed have yet to be seen, exploitation is not very difficult and the chances of attacks being launched in the coming days are high. That is why users have been advised to install the patches from Microsoft as soon as possible, or at least implement the recommended workaround, which involves a registry modification.
The Emergency Directive 20-03 issued by CISA on Thursday instructs federal agencies to take action as soon as possible to ensure that their servers are protected against attacks exploiting CVE-2020-1350.
“CISA has determined that this vulnerability poses unacceptable significant risk to the Federal Civilian Executive Branch and requires an immediate and emergency action,” reads the directive. “This determination is based on the likelihood of the vulnerability being exploited, the widespread use of the affected software across the Federal enterprise, the high potential for a compromise of agency information systems, and the grave impact of a successful compromise.”
Agencies have been given 24 hours to roll out either the patch or the workaround for SIGRed to all Windows DNS servers. They have been given until July 24 to install the patch and remove the workaround, and until the same date they need to ensure that controls are in place so that newly provisioned servers, or ones that have been disconnected, are updated before they are connected to the government’s networks.
Related: CISA Warns Enterprises of Risks Associated With Tor
Related: Patching Pulse Secure VPN Not Enough to Keep Attackers Out, CISA Warns
Related: CISA Reminds Federal Agencies to Use Its DNS Service







You must be logged in to post a comment Login