
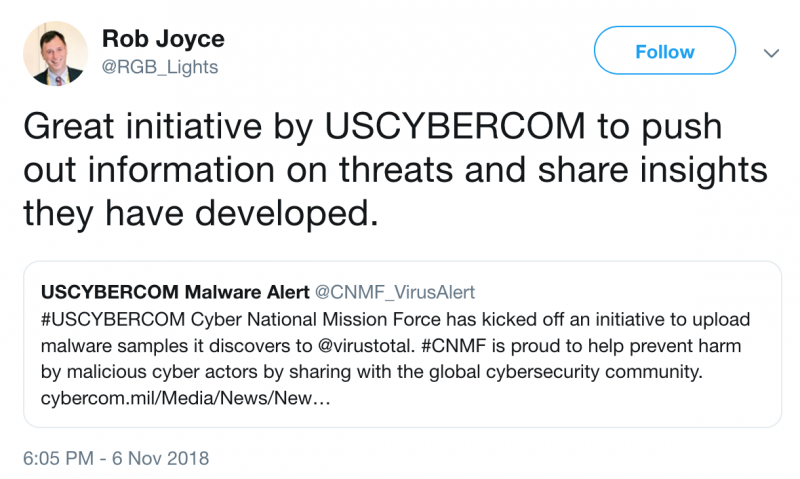
The U.S. Cyber Command (USCYBERCOM) this week started sharing malware samples with the cybersecurity industry via Chronicle’s VirusTotal intelligence service.
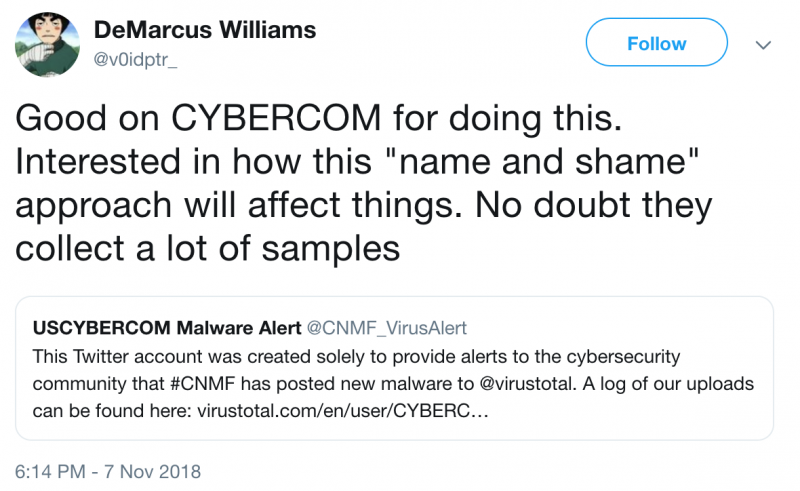
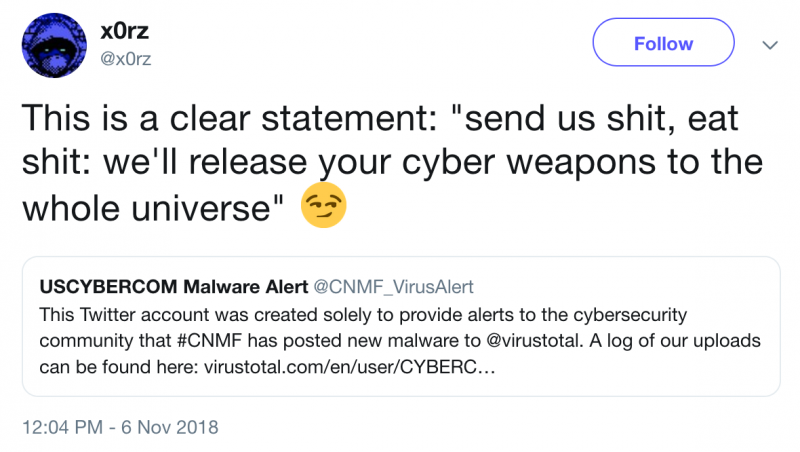
The project is run by USCYBERCOM’s Cyber National Mission Force (CNMF), which will post unclassified malware samples on the CYBERCOM_Malware_Alert account on VirusTotal.
“Recognizing the value of collaboration with the public sector, the CNMF has initiated an effort to share unclassified malware samples it has discovered that it believes will have the greatest impact on improving global cybersecurity,” USCYBERCOM stated.
CNMF claims that its goal is to “to help prevent harm by malicious cyber actors by sharing with the global cybersecurity community.”
Members of the cybersecurity industry can keep track of each new malware sample shared by CNMF through a dedicated Twitter account named USCYBERCOM Malware Alert (@CNMF_VirusAlert). The Twitter account currently has over 3,000 followers and the VirusTotal account is already trusted by more than 50 users.
The first malware samples shared by CNMF on VirusTotal are part of the Lojack (LoJax) family, which researchers observed recently in attacks apparently carried out by the Russia-linked cyber espionage group tracked as Sofacy, APT28, Fancy Bear, Pawn Storm, Sednit and Strontium.
The samples, contained in files named rpcnetp.exe and rpcnetp.dll, seem to be new and related to the UEFI rootkit analyzed by ESET after being used by the Russian threat actor to target government organizations in Central and Eastern Europe.
“So far, the quantity has been small, but the quality is high. Hopefully, these additions from the US Cyber Command will be another useful source of malware which will help the industry to defend against it. However, downloading files requires paid access to VirusTotal Enterprise, so this should be useful for security vendors, but most ‘hobby’ malware analysts won’t have access to the files,” said Chris Doman, security researcher at AlienVault.
Javvad Malik, security advocate at AlienVault, commented, “This is a fantastic new initiative by CNMF. The more threat data the security industry can share amongst itself, the better it can make its defenses. By sharing threat data and samples, security teams can proactively look out for emerging threats and zero days, giving attackers smaller windows of opportunity to conduct successful attacks. It can also be used for threat hunting and to seek out any malware that may have already infiltrated an enterprise. We hope to see more governments and companies share data openly to further the security community’s efforts.”
*Updated with comments from AlienVault
Related: US Military Conducts Cyber Attacks on IS
Related: U.S. Cyber Command Launched DDoS Attack Against North Korea







You must be logged in to post a comment Login