
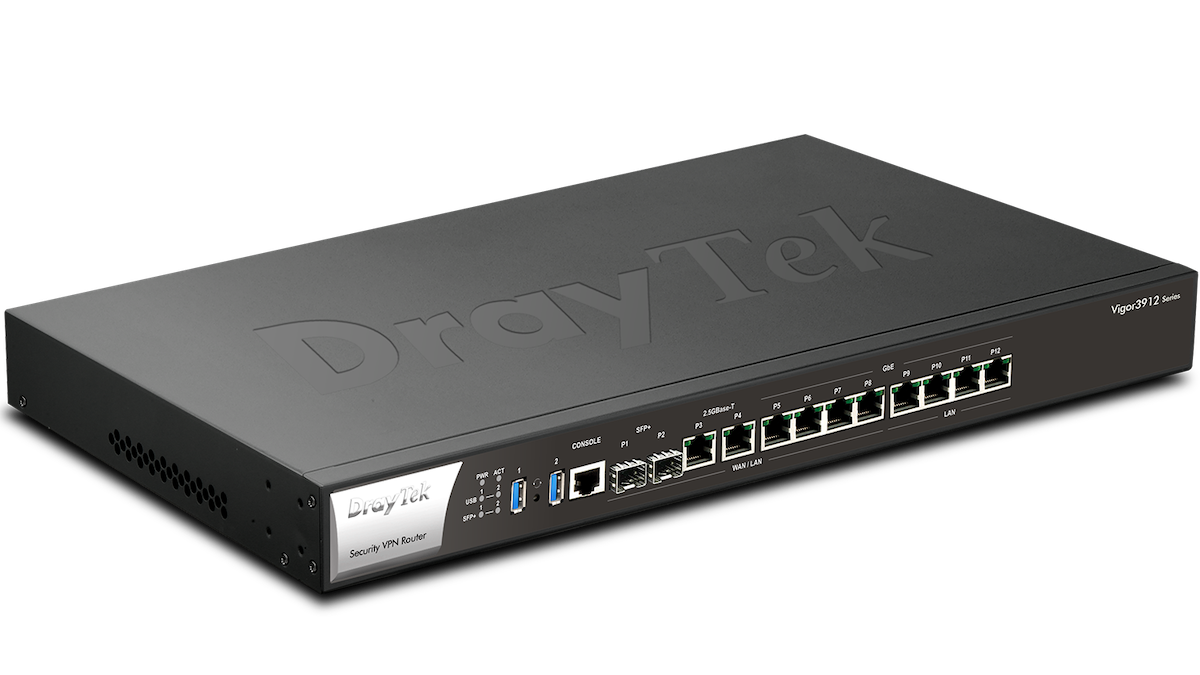
DrayTek on Thursday announced patches for an unauthenticated remote code execution (RCE) vulnerability affecting DrayOS routers.
Tracked as CVE-2025-10547, the issue can be exploited via crafted HTTP or HTTPS requests sent to a vulnerable device’s web user interface.
Successful exploitation of the bug, DrayTek explains in its advisory, may result in memory corruption and a system crash. In certain circumstances, it could be used to execute arbitrary code remotely, it says.
“Routers are shielded from WAN-based attacks if remote access to the WebUI and SSL VPN services is disabled, or if Access Control Lists (ACLs) are properly configured,” DrayTek notes.
“Nevertheless, an attacker with access to the local network could still exploit the vulnerability via the WebUI. Local access to the WebUI can be controlled on some models using LAN side VLANs and ACLs,” the company adds.
The company credited ChapsVision security researcher Pierre-Yves Maes for reporting the vulnerability on July 22.
DrayTek has released firmware updates that address the security defect in 35 Vigor router models, urging users to update their devices as soon as possible. However, it made no mention of the bug being exploited in the wild.
DrayTek devices are widely used by prosumers and SMBs, and are known to be popular targets for hackers. Ransomware groups last year hit hundreds of organizations by exploiting an unknown flaw in DrayTek routers.
Earlier this year, widespread Vigor router reboots reported across the UK, Australia, and other countries were blamed on potentially malicious TCP connection attempts targeting older models.
Related: Organizations Warned of Exploited Meteobridge Vulnerability
Related: Broadcom Fails to Disclose Zero-Day Exploitation of VMware Vulnerability
Related: Cisco Patches Zero-Day Flaw Affecting Routers and Switches
Related: Vulnerabilities Expose Helmholz Industrial Routers to Hacking






