
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

ICS/OT

Siemens Patches DoS Flaws in Medium Voltage Converters

Siemens has released updates for many of its SINAMICS medium voltage converters to address two remotely exploitable denial-of-service (DoS) vulnerabilities.

Siemens has released updates for many of its SINAMICS medium voltage converters to address two remotely exploitable denial-of-service (DoS) vulnerabilities.

According to advisories published by ICS-CERT and Siemens, the flaws impact SINAMICS GH150, GL150, GM150, SL150, SM120 and SM150 converters, which are used worldwide in the energy, chemical, critical manufacturing, water and wastewater, and food and agriculture sectors.Siemens patches two DoS vulnerabilities in SINAMICS medium voltage converters
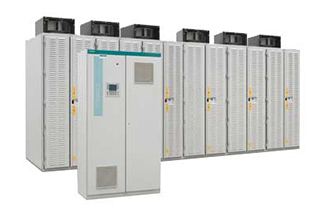
The more serious of the flaws, identified as CVE-2017-12741 and classified “high severity,” can be exploited to cause a DoS condition by sending specially crafted packets to the device on UDP port 161.

The second weakness, tracked as CVE-2017-2680 and rated “medium,” can be exploited by sending specially crafted PROFINET DCP broadcast packets to the targeted device. This issue is less serious due to the fact that exploitation requires direct Layer 2 access to the impacted product. Siemens noted that PROFIBUS interfaces are not affected.

In both cases, manual intervention is required to restore the device after it has entered a DoS condition.

Learn More at SecurityWeek’s 2018 ICS Cyber Security Conference

The vulnerabilities can be patched by updating the firmware to versions 4.7 SP5 HF7, 4.7 HF30 or 4.8 SP2. Siemens says attacks involving CVE-2017-12741 can also be mitigated by blocking network access to port 161.

Advertisement. Scroll to continue reading.

While in general DoS vulnerabilities may not pose a major risk, these types of weaknesses can have a significant impact in industrial environments, where availability is often crucial.

Related: Serious Flaw Found in Many Siemens Industrial Products

Related: Severe Flaws Expose Moxa Industrial Routers to Attacks

Related: Internet Exposure, Flaws Put Industrial Safety Controllers at Risk of Attacks

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Close the security gaps between pentests. Join this session to explore agentic pentesting and gain a practical framework for continuous exposure validation in your CTEM program.

Register

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

People on the Move

Barracuda has appointed Dan Fletcher as CFO.

Artemis Security has appointed Arun Singh as CGO.

General Paul M. Nakasone has joined Armadin’s Board of Directors.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





