
SAP’s security updates for November 2020 patch several critical vulnerabilities affecting the company’s Solution Manager (SolMan), Data Services, ABAP, S4/HANA, and NetWeaver products.
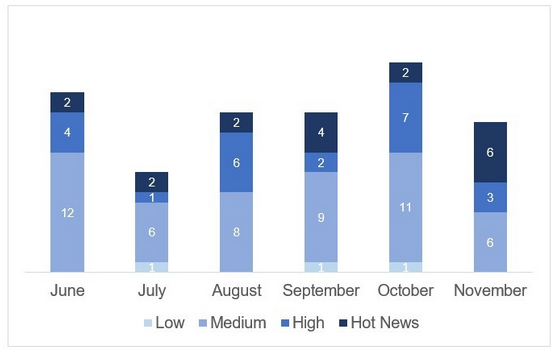
Since the previous Patch Day, SAP released a total of 19 new and updated security notes. Six of the notes have been assigned a hot news (critical) priority rating, including four new notes and two previously released patches that were updated.
One of the hot news patches resolves a total of four vulnerabilities related to missing authentication checks in SolMan, which provides a central management interface for SAP and non-SAP systems. An unauthenticated attacker could exploit these flaws — they are tracked as CVE-2020-26821, CVE-2020-26822, CVE-2020-26823 and CVE-2020-26824 — to compromise the targeted system.
SAP has also updated a previous hot news security note that addressed a missing authentication check in SolMan.
“We have once more seen that Solution Manager will keep security administrators busy, because of its central role in the system landscape and the criticality of the newly detected vulnerabilities,” said Onapsis, a company that specializes in securing business-critical applications.
Onapsis has published a blog post describing this month’s patches, some of which fix vulnerabilities found by the company’s own researchers.
Another hot news patch addresses two vulnerabilities in SAP Data Services. These flaws were disclosed last year and they impact Apache Struts. Exploitation can lead to remote code execution and a denial-of-service (DoS) condition, respectively.
A code injection vulnerability affecting SAP AS ABAP and S/4 HANA (CVE-2020-26808) and a privilege escalation issue in SAP NetWeaver Application Server for Java (CVE-2020-26820) have also been rated hot news.
Three of the new patches address high-severity vulnerabilities, including server-side request forgery (SSRF) and reflected cross-site scripting (XSS) issues in SAP Fiori Launchpad, an information disclosure issue in SAP Commerce Cloud, and DoS and SSRF bugs in Commerce Cloud.
Medium-severity flaws have been resolved in NetWeaver, Bank Analyzer, S/4 HANA Financial Products, SAP Process Integration, ERP Client for E-Bilanz, and Visual Enterprise Viewer.
Related: SAP Patches Critical Vulnerability in CA Introscope Enterprise Manager
Related: Critical Access Control Vulnerability Patched in SAP Marketing
Related: SAP Releases August 2020 Security Updates
Related: Open Source Tool Checks SAP Systems for RECON Attack IOCs







You must be logged in to post a comment Login