
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

ICS/OT

Rockwell Controller Flaw Allows Hackers to Redirect Users to Malicious Sites

A serious vulnerability affecting some of Rockwell Automation’s MicroLogix and CompactLogix programmable logic controllers (PLCs) can be exploited by a remote attacker to redirect users to malicious websites.

A serious vulnerability affecting some of Rockwell Automation’s MicroLogix and CompactLogix programmable logic controllers (PLCs) can be exploited by a remote attacker to redirect users to malicious websites.

According to advisories published by ICS-CERT and Rockwell Automation, the flaw, tracked as CVE-2019-10955 and assigned a CVSS score of 7.1 (high severity), impacts MicroLogix 1100 and 1400, and CompactLogix 5370 (L1, L2 and L3) controllers.
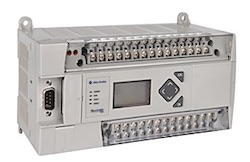
Rockwell patches open redirect vulnerability in PLCThe issue, described by ICS-CERT as an open redirect vulnerability, is related to the web server running on these devices. This web server accepts user input from the PLCs web interface and a remote, unauthenticated attacker can inject a malicious link that redirects users from the controller’s web server to an arbitrary site.

“This malicious website could potentially run or download arbitrary malware on the user’s machine. The target of this type of attack is not the industrial control device and does not disrupt its control functionality,” Rockwell noted in its advisory (only available to registered users).

Learn More About ICS Flaws at SecurityWeek’s 2019 ICS Cyber Security Conference

The vendor has released firmware updates for the affected controllers that should patch the vulnerability. Organizations that cannot install the updates have been advised to disable the web server and implement general security measures in order to prevent potential attacks.

Researchers Josiah Bryan and Geancarlo Palavicini have been credited for reporting the vulnerability to Rockwell Automation.

Advertisement. Scroll to continue reading.

Related: Severe Vulnerabilities Expose MicroLogix PLCs to Attacks

Related: Rockwell Automation Patches Serious Flaw in MicroLogix 1400 PLC

Related: Vulnerability Exposes Rockwell Controllers to DoS Attacks

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Close the security gaps between pentests. Join this session to explore agentic pentesting and gain a practical framework for continuous exposure validation in your CTEM program.

Register

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

People on the Move

Quantum eMotion has named Wayne Teeple as CTO.

Guy Ellis has been appointed CEO of NCC Group.

Noma Security has named Bobby Shoker as CFO and Alberto Rodrigues as CCO.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





