
At least two threat groups have started exploiting a critical Oracle WebLogic vulnerability patched earlier this month. The attacks began shortly after several proof-of-concept (PoC) exploits were made public.
The vulnerability, tracked as CVE-2018-2893 and assigned a CVSS score of 9.8, allows an unauthenticated attacker to remotely take control of a WebLogic Server. The flaw affects the product’s WLS Core Components subcomponent and it can be exploited via the T3 transport protocol.
The security hole impacts versions 10.3.6.0, 12.1.3.0, 12.2.1.2 and 12.2.1.3, and it was addressed by Oracle with its July 2018 Critical Patch Update (CPU).
Oracle has credited five different researchers for independently reporting the flaw, and one of the experts already claims to have found a way to bypass the vendor’s patch.
Shortly after Oracle announced the latest security updates on July 18, several individuals released PoC exploits on GitHub and other websites.
The Netlab group at Chinese security company Qihoo 360 reported seeing the first attacks on July 21. The campaign used luoxkexp[.]com as its main command and control (C&C) server.
According to NetLab, the domain was registered in March 2017 and hackers have been using it ever since. The group that owns the domain, tracked by NetLab as luoxk, has been using it for campaigns involving DDoS bots, RATs, cryptocurrency mining, malicious Android APKs, and worm-style exploits with the Java RMI (Remote Method Invocation) service.
In the attacks involving CVE-2018-2893, the hackers delivered the XMRig Monero miner and the Bill Gates DDoS malware.
SANS has also tracked attacks exploiting CVE-2018-2893 and the organization has seen attempts to install what appears to be a backdoor.
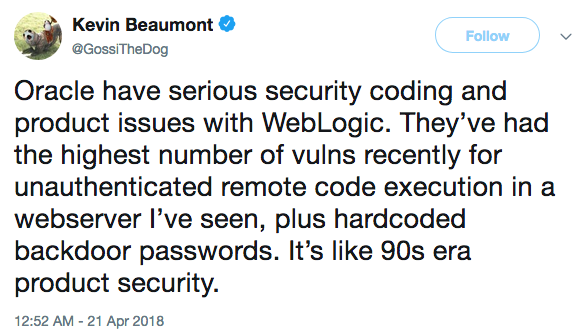
It’s not uncommon for malicious actors to target Oracle WebLogic vulnerabilities in their attacks, with several campaigns spotted over the past months.
While Oracle has been busy developing patches for these flaws, researchers have managed to find ways to bypass the fixes.
Related: Oracle Fixes Spectre, Meltdown Flaws With Critical Patch Update
Related: Oracle Patches New Spectre, Meltdown Vulnerabilities






