
CONFERENCE CISO Forum Virtual Summit 2026 - View all Sessions
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Cybercrime

Recently Patched Confluence Vulnerability Exploited in the Wild

Hackers started exploiting a vulnerability in Atlassian’s Confluence enterprise collaboration product just one week after the availability of a patch was announced.

Hackers started exploiting a vulnerability in Atlassian’s Confluence enterprise collaboration product just one week after the availability of a patch was announced.

Atlassian informed customers on August 25 that Confluence is affected by a critical vulnerability — described as an OGNL injection issue — that can allow remote attackers to execute arbitrary code on impacted Confluence Server and Data Center instances.

The flaw, tracked as CVE-2021-26084, can in some cases be exploited without authentication. Patches are included in versions 6.13.23, 7.4.11, 7.11.6, 7.12.5 and 7.13.0.

On August 29, researchers said it was easier than expected to reproduce the exploit. On September 1, cybersecurity companies started seeing internet scans aimed at identifying vulnerable systems, as well as exploitation attempts.

Threat intelligence company Bad Packets has observed attacks exploiting CVE-2021-26084 to deliver cryptocurrency miners.
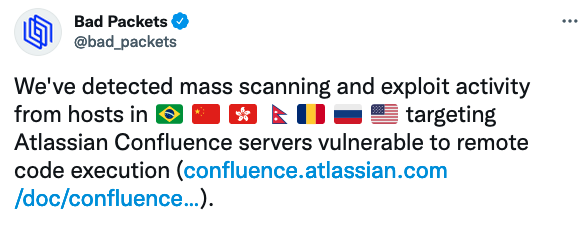
CVE-2021-26084 exploited

After the first in-the-wild exploitation attempts were spotted, researchers released a technical analysis of the vulnerability and proof-of-concept (PoC) exploit code, which will likely lead to even more threat groups adding the Confluence vulnerability to their arsenal.

Advertisement. Scroll to continue reading.

Government cybersecurity agencies started issuing alerts for CVE-2021-26084 after the first exploitation attempts were observed.

Both profit-driven cybercriminals and state-sponsored threat actors have been known to target vulnerabilities in Atlassian products.

Related: Atlassian Patches Critical Vulnerability in Jira Data Center Products

Related: Researchers Detail Exploit Chain for Hijacking Atlassian Accounts

Related: AESDDoS Botnet Targets Vulnerability in Atlassian’s Confluence Server

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Jensen Huang has resigned as President and Chief Executive Officer at NVIDIA.

Sean Sweeney has become CIO of the City of Charleston, South Carolina.

Commerce has appointed Amalie Combs as CISO.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





