
The RansomHub ransomware group over the weekend claimed responsibility for the April 2024 cyberattack on telecommunications giant Frontier Communications.
In an April filing with the Securities and Exchange Commission (SEC), Frontier revealed that the intrusion was identified on April 14 and resulted in certain systems being shut down to contain the attack.
In a quarterly report filed with the SEC in May, the Dallas-based company reiterated that the attackers likely stole certain data from its systems, including personal information.
“Based on our investigation, we have determined that the third party was likely a cybercrime group, which gained access to, among other information, personally identifiable information,” Frontier said.
The telecoms giant also reiterated that the disruption caused by the attack could be considered material, said that it believed it had restored the impacted systems, and noted that it did not believe the incident would have a material impact on its financial condition.
While the company shared no additional information on the number of potentially affected individuals, the RansomHub gang added Frontier on its leak site over the weekend, claiming to have stolen 5GB of data from the company.
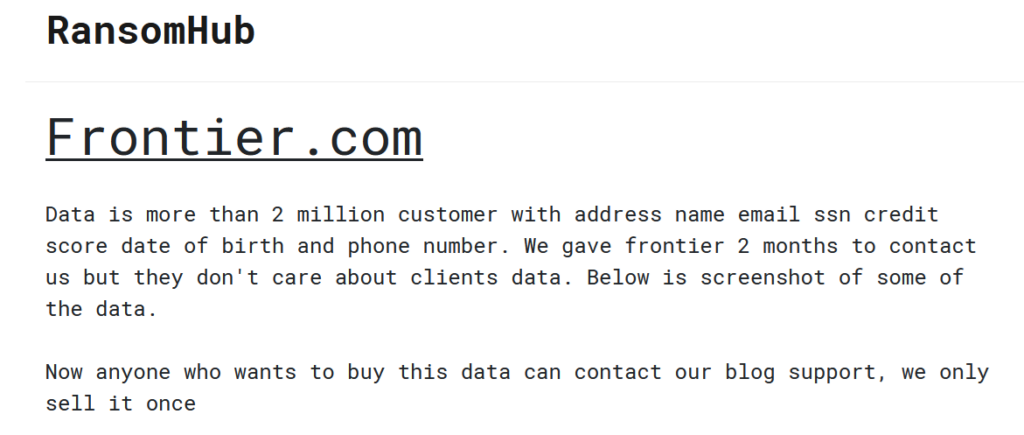
The stolen information, the ransomware group claims, includes the names, addresses, dates of birth, phone numbers, email addresses, Social Security numbers, and credit scores of more than two million Frontier customers.
RansomHub has published a screenshot as proof of possession and threatens to sell it to anyone interested or share it publicly within ten days.
A relatively new ransomware group, RansomHub came to fame in April, when it added UnitedHealth Group’s subsidiary Change Healthcare to its leak site. In February, Change Healthcare was hacked by a BlackCat affiliate who joined RansomHub after the BlackCat operator pulled an exit scam.
Last month, the ransomware group claimed responsibility for a cyberattack on auction house Christie’s.
Related: Ransomware Attack Disrupts Seattle Public Library Services
Related: Ukrainian REvil Ransomware Affiliate Gets 13 Years in US Prison
Related: New macOS Backdoor Linked to Prominent Ransomware Groups






