
The Port of Seattle is notifying 90,000 individuals that their personal information was compromised in an August 2024 data breach resulting from a ransomware attack.
The incident occurred on August 24 and forced the Port to isolate critical systems, which impacted the Seattle-Tacoma International Airport (SEA Airport), Fishermen’s Terminal, and public marinas it operates.
In mid-September, the Port confirmed that ransomware was used in the attack, blaming the Rhysida group for the intrusion and announcing that it refused to pay a ransom. The threat actor was demanding a $6 million ransom to be paid.
Rhysida added the Port to its Tor-based website a couple of days later, claiming the theft of over 3 TB of data that was offered for auction. The ransomware group has since made some of the data available publicly.
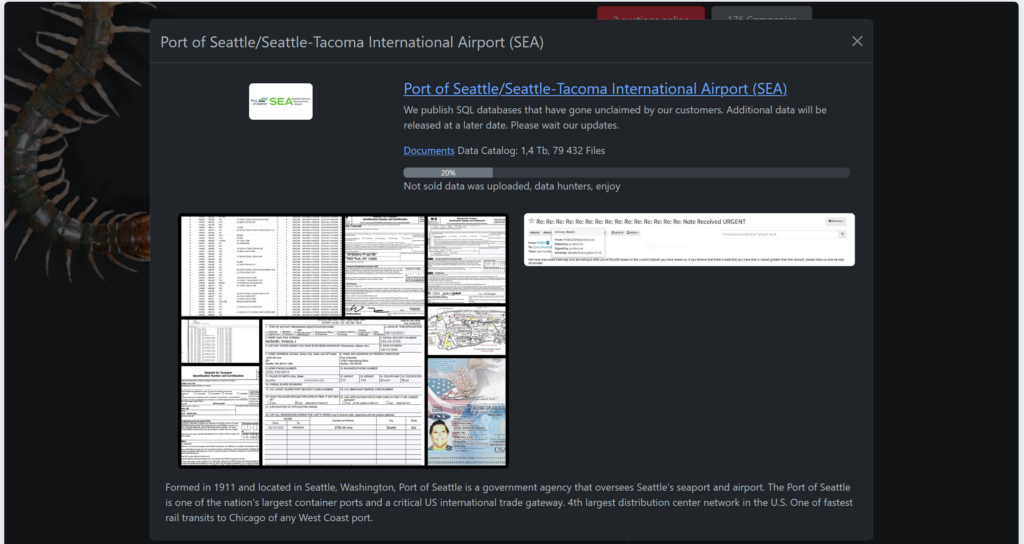
On April 3, the Port revealed that personal information such as names, dates of birth, Social Security numbers, driver’s license numbers, other government ID numbers, and medical information was stolen in the attack.
“The threat actors accessed and downloaded some personal information from Port systems, primarily legacy ones used for employee, contractor, and parking data. The Port holds very little information about airport or maritime passengers, and systems processing payments were not affected,” the Port said.
According to the Port, 90,000 individuals were affected, most of which are “current and former Port and other airport employees and contractors. Roughly 71,000 of the impacted people live in Washington state.
The Port is providing the impacted individuals with one year of free credit monitoring and identity theft protection services.
It also underlines that the incident did not affect the proprietary systems of airlines, cruise, and federal partners, and that the attack did not “affect the ability to safely travel to or from Seattle-Tacoma International Airport or safely use the Port’s maritime facilities”.
Related: State Bar of Texas Says Personal Information Stolen in Ransomware Attack
Related: Hunters International Ransomware Gang Rebranding, Shifting Focus
Related: Ransomware Group Takes Credit for National Presto Industries Attack
Related: Russian Espionage Group Using Ransomware in Attacks






