
Over 70% of the industrial control system (ICS) vulnerabilities disclosed in the first half of 2020 were remotely exploitable through a network attack vector, industrial cybersecurity company Claroty reported on Wednesday.
Claroty has analyzed the 365 ICS flaws added to the National Vulnerability Database (NVD) and 385 vulnerabilities covered in advisories published by ICS-CERT (CISA). The security holes affect products from a total of 53 vendors and nearly three quarters of them were identified by security researchers.
Claroty told SecurityWeek that it has decided to analyze both vulnerabilities covered in ICS-CERT advisories and the NVD to “get the most comprehensive data about the state of security of ICS products.” While many of the advisories overlap, there are some discrepancies.
“Based on our research we have seen cases that some ICS-related CVEs are not covered 100% by the ICS-CERT advisories but are shown in the NVD, and vice versa,” explained Amir Preminger, VP of Research at Claroty. “In future reports we are planning to expand our covered sources since we have found that more information can be collected from different CERTs and vendor advisories.”
Learn more about ICS vulnerabilities at SecurityWeek’s 2020 ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series
The number of vulnerabilities added to the NVD in the first half of 2020 is roughly 10% higher compared to the number of flaws disclosed in the same period of 2019. ICS-CERT published 139 advisories, compared to 105 in the first half of the previous year.
“While it may seem logical to assume that this and similar increases were caused by an increase in adversary activity and/or a decrease in ICS vendors’ security posture, the primary factors are likely heightened awareness of the risks posed by ICS vulnerabilities and increased focus from researchers and vendors on identifying and remediating such vulnerabilities as effectively and efficiently as possible,” Claroty explained in its report.
According to the company, the fact that over 70% of the vulnerabilities covered in the NVD can be exploited remotely shows that fully air-gapped industrial networks that are better protected against cyber threats have become “vastly uncommon.”
Nearly half of the identified vulnerabilities can be exploited for remote code execution, 41% of them can allow an attacker to read application data, 39% can be exploited for DoS attacks, and 37% to bypass security mechanisms.
In the case of the advisories published by ICS-CERT, more than 81% impact products used worldwide, and 7% of the advisories are for products used exclusively in the U.S.
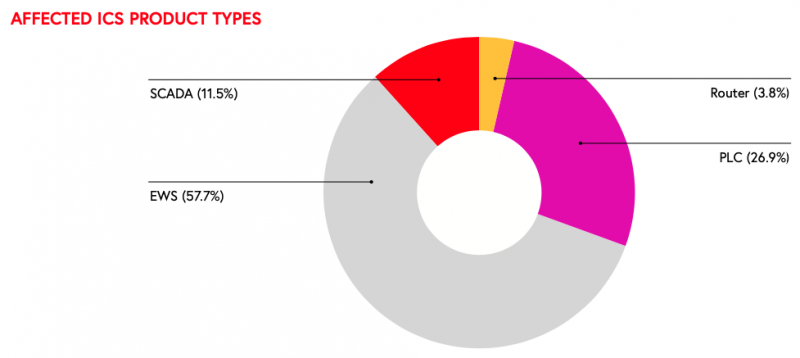
The sectors most impacted by these vulnerabilities are energy (236 vulnerabilities), critical manufacturing (197), and water and wastewater (171). These were also the top three sectors last year, but the number of flaws affecting them is now much higher.
Related: Industrial Cybersecurity Firm Claroty Releases Open Source Database Parser
Related: Many ICS Vulnerability Advisories Contain Errors: Report







You must be logged in to post a comment Login