
The number of vulnerabilities discovered in industrial control system (ICS) products in 2020 increased significantly compared to previous years, according to a report released on Thursday by industrial cybersecurity firm Claroty.
According to Claroty, the number of ICS vulnerabilities disclosed in 2020 (893 vulnerabilities) was nearly 25% higher compared to 2019 and close to 33% higher than in 2018. The company believes this increase is likely the result of heightened awareness of the risks posed by vulnerabilities in industrial products, as well as researchers and vendors putting more effort into identifying and patching security holes.
The company said 61% of vulnerabilities were discovered by third-party researchers, many of them employed by cybersecurity companies.
Learn more about vulnerabilities in industrial systems at SecurityWeek’s 2020 ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series
Claroty’s report, which focuses on the second half of 2020, reveals that, similar to the first half of the year, roughly 70% of the identified flaws can be exploited remotely. Also similar to the first half, the security holes were found in the products of more than 50 vendors. More than 70% of the bugs disclosed in H2 were rated critical or high severity, down from over 75% in H1.
In terms of industries, Claroty said the most impacted in the second half of 2020 were critical manufacturing (194 vulnerabilities), energy (186), water and wastewater (111), and commercial facilities (108).
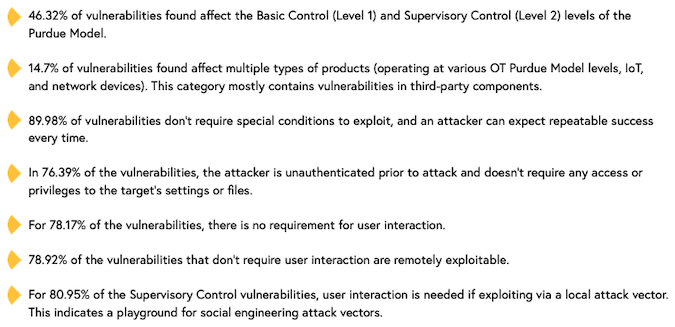
“The steady growth of reported ICS vulnerabilities is noteworthy in terms of maturation, but currently, it’s also largely limited to three vendors: Schneider, Mitsubishi, and Siemens. A large majority of the products with disclosed and patched vulnerabilities in the 2H of 2020 belong to those three leading vendors; the remaining vendors had combined relatively fewer products affected by vulnerabilities,” Claroty said in its report.
It added, “Does this mean that the smaller number of vendors we looked at have cleaner, more secure products? Likely, no. Instead, it’s more of an issue of accessibility to equipment for a growing number of researchers; market leaders have an abundance of equipment inside organizations that can be assessed for security flaws. Some of this gear that has been retired can also be purchased on eBay and other platforms for research purposes.”
Related: Over 12% of ICS Security Incidents Attributed to Nation-State Hackers
Related: Manufacturing Sector Targeted by Five ICS-Focused Threat Groups
Related: Pandemic Leads to Rise in Industrial Systems Targeted Via RDP: Report
Related: Hundreds of Industrial Organizations Received Sunburst Malware in SolarWinds Attack







You must be logged in to post a comment Login