
Facebook on Thursday said it recently disabled billions of bogus accounts set up by "bad actors" and that five percent of active accounts are likely fakes.



Hi, what are you looking for?

Facebook on Thursday said it recently disabled billions of bogus accounts set up by "bad actors" and that five percent of active accounts are likely fakes.
The hacking of U.S. election systems, including by foreign adversaries, is inevitable, and the real challenge is ensuring the country is resilient enough to withstand catastrophic problems from cyber breaches, government officials said Wednesday.
SandboxEscaper, the security researcher who posted a claimed zero-day Windows 10 vulnerability on GitHub Tuesday, has now posted the remaining four exploits (two yesterday and the final two today) that he or she (we'll say 'she') said she possessed.
Instagram on Thursday said it was not the source of private contact information for millions of influential users of the service recently found in an unguarded online database.
Siemens and Alphabet-owned cybersecurity firm Chronicle this week announced a partnership whose goal is to provide industrial monitoring and detection solutions for the energy sector.
The head of NATO told Russia and other potential foes Thursday that the Western military alliance was ready to use all means at its disposal to respond to cyber attacks.Jens Stoltenberg's warning came with the bloc's members on alert for interference in European Parliament elections that kicked off in Britain and the Netherlands on Thursday.
Gartner’s latest IT spending forecast predicts that spending on data center systems will reach $195 billion in 2019, but decrease to $190 billion through 2022. In contrast, spending on cloud infrastructure services will grow from $39.5 billion in 2019 to $63 billion through 2021. This cloud shift would be even more pronounced if many organizations still weren’t reluctant to embark on cloud transformation projects or concerned about security risks of moving workloads to the cloud.
Comodo CA (now known as Sectigo) is the Certificate Authority (CA) that issued the largest number of digital certificates used to sign malware samples found on VirusTotal over the past year, Chronicle’s security researchers have discovered.
Authorities in Europe this week said they took down Bestmixer.io, one of the leading cryptocurrency mixing service in the world. The takedown was possible due to a collaboration between the Dutch Fiscal Information and Investigation Service (FIOD), Europol, and authorities in Luxembourg.
Several proof-of-concept (PoC) exploits, including ones that can be used for remote code execution, have been developed for the recently patched Windows Remote Desktop Services (RDS) vulnerability tracked as CVE-2019-0708 and dubbed BlueKeep.
Moody's has revised its Equifax outlook from stable to negative, citing the effect of the 2017 data breach. This is the first time that a cybersecurity incident has resulted in a Moody's outlook downgrading.
You may find it surprising that small businesses make up more than 97% of total businesses in North America, according to the Better Business Bureau (BBB). Given this statistic, I suppose the good news is that fewer than half of all cyberattacks target small businesses. The bad news is that when small/midmarket businesses (SMBs) are attacked, the majority don’t survive. But this doesn’t have to be the case.
Britain has shared with 16 NATO allies details of malicious Russian cyber activity in their countries over the last 18 months, foreign minister Jeremy Hunt was to say on Thursday.
Amazon on Wednesday confirmed that shareholders rejected proposals to prohibit sales of facial recognition technology to governments and study how it might threaten privacy or civil rights.
On May 25, 2018 the General Data Protection Regulation came into law for European Union countries, created to protect data relating to E.U. citizens, ensuring the right to know what is being stored, where and why.
Researchers at Cambridge University have determined that attackers could use the built-in motion sensors in mobile devices to generate a unique device fingerprint.
Tens of very basic but Critical vulnerabilities were found in 10 South Korean ActiveX controls as part of a short research project, security researchers with Risk Based Security say.
Microsoft-owned social media giant LinkedIn has once again put user data and privacy at risk by allowing a TLS certificate to expire.
The skimmer used in a recently discovered Magecart attack on a Magento-based e-commerce website was posing as a payment service provider via a rogue iframe, Malwarebytes reports.
One year after the entry into force of landmark EU rules to better protect personal data, nearly 145,000 complaints have been registered, an initial assessment revealed on Wednesday.

The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.




The top payout is for high-impact architectural research demonstrating full administrative control.


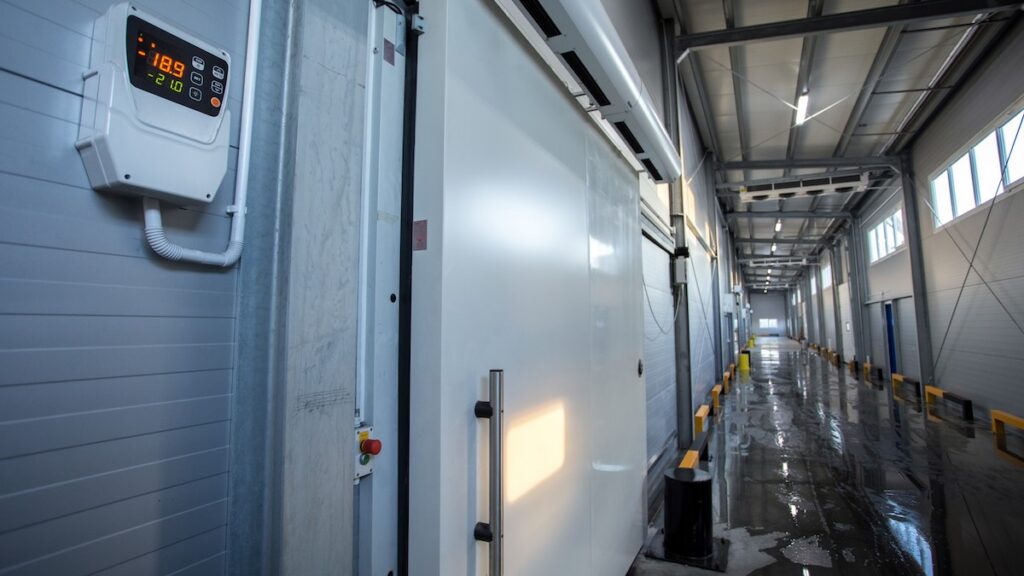
The recommendations come amid attacks targeting fridges and freezers in supermarkets and blood banks in Europe.