
Law enforcement agencies in the US and Europe targeted the cybercrime service that has impacted 360,000 devices since 2020.
Hi, what are you looking for?

Law enforcement agencies in the US and Europe targeted the cybercrime service that has impacted 360,000 devices since 2020.
The flaws can be exploited to manipulate data and bypass security restrictions, potentially leading to code execution.
The company has released iOS and iPadOS versions 16.7.15 and 15.8.7 to patch the vulnerabilities.
The social media giant has disabled more than 150,000 accounts powering scam centers in Asia.
The issue allows attackers to inject SQL queries and extract sensitive information from the database.
Applying SOC-level rigor to the rumors, politics, and 'human intel' can make or break a security team.
Critical- and high-severity flaws could be exploited to execute arbitrary shell commands or elevate privileges.
The security defects could lead to denial-of-service (DoS) conditions, command execution, or device takeover.
The bugs allowed unauthenticated attackers to execute arbitrary code, steal credentials, and take over servers.
The 2024 incident was initially linked to China, but an infostealer infection has now revealed North Korean involvement.
The leadership structure, commonly referred to as the “dual-hat” arrangement, assigns a single individual to oversee both organizations.
Stryker was targeted by the Handala group, which claims to have wiped more than 200,000 of the company’s devices.
Google has completed its $32 billion acquisition of the cloud security giant, which will maintain its brand.
Cardwell started her career at Netscape, become a VP of engineering at American Express, CISO at UnitedHealth Group, and now CISO in Residence at Transcend.
Hackers stole personal information such as names, Social Security numbers, and driver’s license numbers.
The company connects AI agents to security data lakes for interactive investigations, detection engineering, and autonomous response.
Promptfoo has raised more than $23 million in funding for a platform that helps developers secure LLMs and AI agents.
The bugs could lead to arbitrary code execution, privilege escalation, or authentication rate-limit bypass.
The evolution of vulnerability management in the agentic era is characterized by continuous telemetry, contextual prioritization and the ultimate goal of agentic remediation.
The cybercriminals have leaked more than 300GB of files allegedly stolen from the tire giant.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
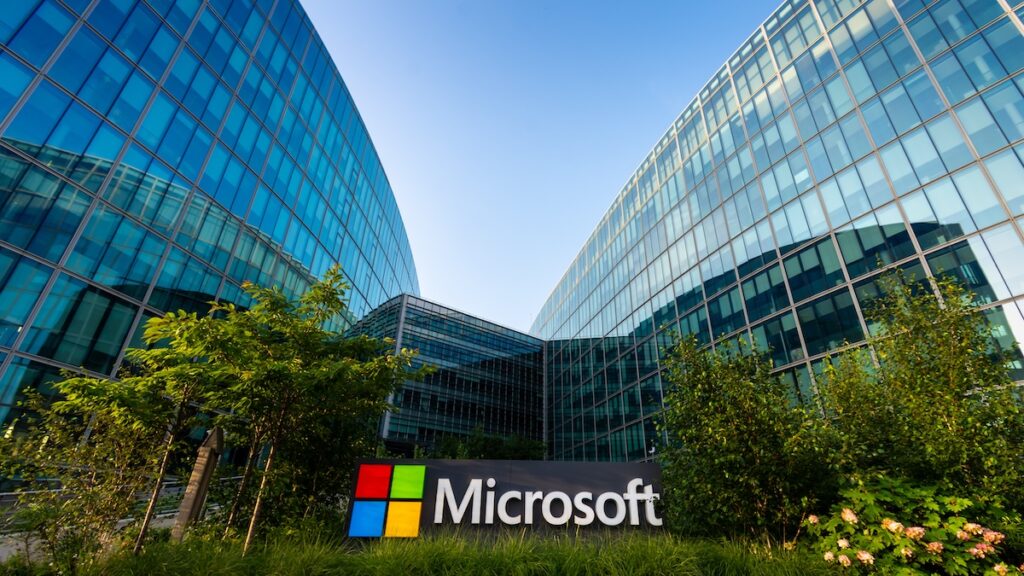
A total of 22 patches were releaased, a majority for code execution, privilege escalation, and information disclosure vulnerabilities.

AVEVA and Rockwell Automation also released patches for vulnerabilities affecting industrial control system products.