
Siemens this week announced the availability of patches and mitigations for a series of severe vulnerabilities that can be exploited to remotely crash some of the company’s SIMATIC products.
The German industrial giant released nine advisories on Tuesday to address a total of 27 vulnerabilities. One of these advisories describes three high-severity flaws that can be exploited by a remote, unauthenticated attacker to launch denial-of-service (DoS) attacks against some Siemens programmable logic controllers (PLCs) and associated products.
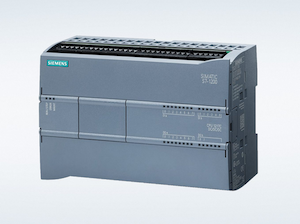 The security holes are tracked as CVE-2021-37185, CVE-2021-37204 and CVE-2021-37205, and they can be exploited by sending specially crafted packets over TCP port 102 to the targeted device. If a vulnerability has been exploited successfully, the device needs to be restarted in order to restore normal operations.
In a real world industrial environment, crashing a PLC can have a serious impact and cause significant disruption.
Siemens says the flaws impact SIMATIC S7-1200 and S7-1500 PLCs, SIMATIC Drive Controller, ET 200SP Open Controller, S7-1500 Software Controller, SIMATIC S7-PLCSIM Advanced, the TIM 1531 IRC communication module, as well as SIPLUS extreme products.
Independent ICS security researcher Gao Jian, who has been credited by Siemens for reporting the vulnerabilities, told SecurityWeek that these are just some of the eight vulnerabilities that he has reported to the vendor. The remaining issues are under investigation. The researcher started reporting his findings to Siemens in early August 2021.
Jian explained in an advisory that the vulnerabilities, which he has dubbed S7+:Crash, are related to the OMS+ communication protocol stack used by Siemens products.
Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference
Siemens PLCs can be protected against unauthorized operations by enabling an access level option and setting a password. However, the researcher says the attack methods he has identified work even if the “complete protection” option is selected.
Moreover, Jian says, the flaws can be exploited even if a recently introduced feature designed to secure communications between PLCs and PCs or HMIs is enabled.
The “S7+:Crash” vulnerabilities can be exploited by a threat actor who has access to the targeted device on TCP port 102. Exploitation directly from the internet may also be possible if the PLC is exposed due to a misconfiguration.
“Note that even the SIMATIC products enabled with access protection and secure communication (TLS encryption) cannot mitigate these vulnerabilities, and there is no firewall capable of parsing the S7CommPlus_TLS protocol, making it very difficult to prevent such attacks,” Jian explained.
The researcher has published a video showing his exploit in action.
Related: Newly Disclosed Vulnerability Allows Remote Hacking of Siemens PLCs
Related: Siemens Releases Several Advisories for ‘NAME:WRECK’ Vulnerabilities
Related: Siemens Addresses Code Execution Vulnerabilities Found in Popular CAD Library







You must be logged in to post a comment Login