
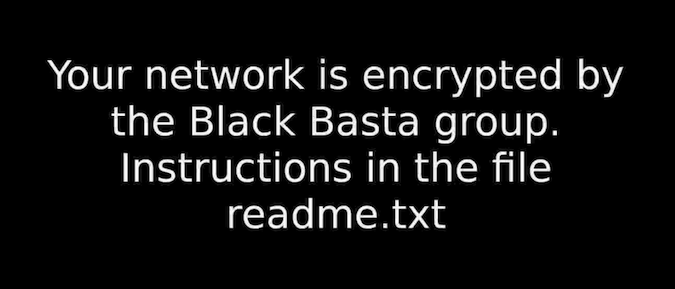
A new ransomware operation named Black Basta has targeted at least a dozen companies and some researchers believe there may be a connection to the notorious Conti group.
The existence of Black Basta came to light in mid-April, but MalwareHunterTeam researchers spotted a sample apparently compiled in February.
The cybercriminals behind Black Basta use malware to encrypt files on compromised systems, appending the .basta extension to encrypted files. In addition, like many other ransomware groups, they steal large amounts of information from victims in an effort to increase their chances of getting paid.
Cybersecurity firm Minerva has conducted a technical analysis of the Black Basta ransomware and noted that the malware requires administrator privileges to work. The company’s researchers discovered that the malware hijacks the Windows Fax service for persistence on the infected systems.
The Black Basta group has listed roughly a dozen companies on its website, where it names victims that refuse to pay up. The list of victims includes the American Dental Association and German wind turbine giant Deutsche Windtechnik, which recently confirmed the breach, but claimed its wind turbines were never at risk.
The hackers have published more than 100 Gb of data allegedly stolen from Deutsche Windtechnik.
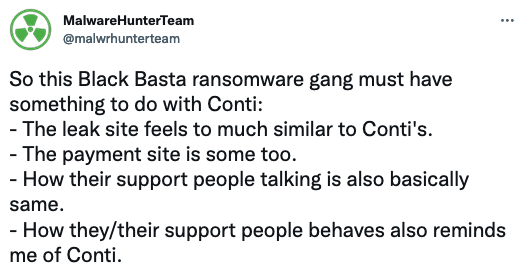
MalwareHunterTeam believes the “Black Basta ransomware gang must have something to do with Conti.” This assumption is based on similarities between their leak sites, their payment sites, and the way their “support” employees talk and behave. Other researchers agree that there are similarities to the Conti operation.
In the meantime, the Conti group continues announcing new targets, including government organizations in Peru and Costa Rica.
In fact, Conti ransomware activity has surged in the past weeks, despite the cybercriminals’ operations being exposed by a pro-Ukraine hacktivist.
The hacktivist used a Twitter account named “ContiLeaks” to make available chat logs, credentials, email addresses, C&C server details and even source code from the Conti operations. The leaks came in response to the Conti group expressing its support for the Russian government in its invasion of Ukraine.
While some believed the leaks could hurt Conti operations, Secureworks reported recently that the number of new victims added to Conti’s website in March 2022 exceeded 70, significantly more than the average of 43 victims per month seen in 2021.
Related: Walmart Dissects New ‘Sugar’ Ransomware
Related: Colossus Ransomware Hits Automotive Company in the U.S.
Related: FBI Shares Information on BlackCat Ransomware Attacks







You must be logged in to post a comment Login