Mortgage giant Mr. Cooper on Thursday announced that it has shut down certain systems after falling victim to a cyberattack, which resulted in its operations being suspended.
The attack occurred on October 31 and prompted an immediate response, including containment measures that involved taking down some systems.
“Mr. Cooper Group determined on October 31, 2023 that the company experienced a cybersecurity incident in which an unauthorized third party gained access to certain technology systems,” the company said, responding to a SecurityWeek inquiry.
“We value our customers and take their data privacy very seriously, and we have launched an investigation with assistance from leading cybersecurity experts and notified law enforcement,” the company said.
The shutdown, the company says in an incident notice on its website, prevents it from processing customer payments temporarily, but such operations will resume as soon as systems are restored.
“If you use ACH, your payment will be processed as soon as our systems are operational and you will receive a notification. You do not need to do anything. If you use any other method of payment, you will be able to do so as soon as we resolve this issue,” the company notes.

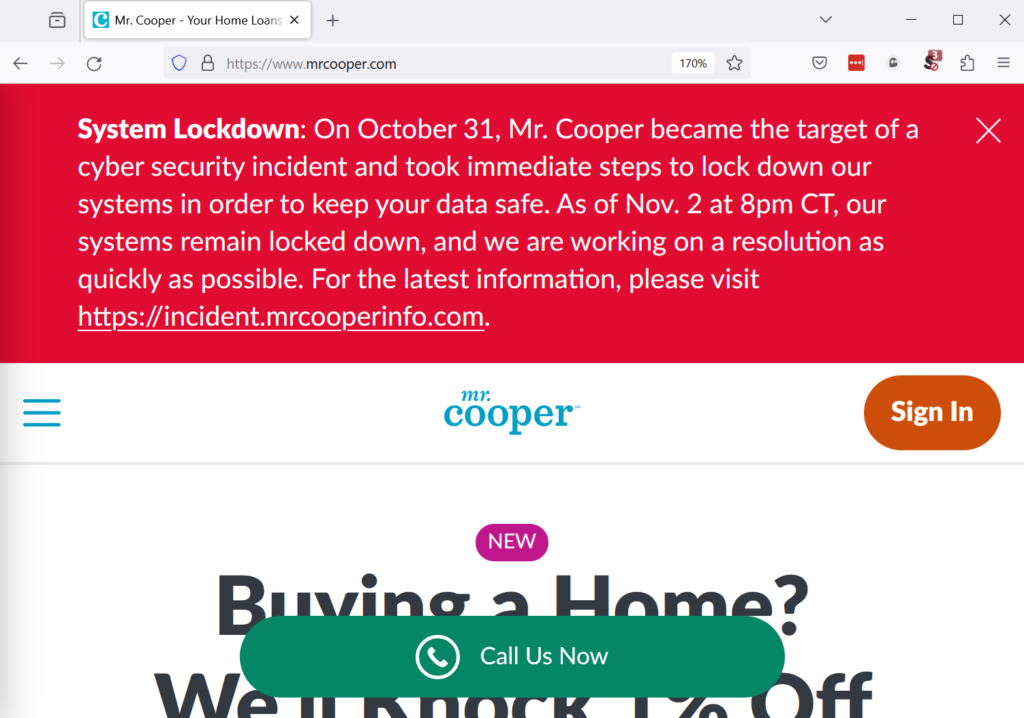
Mr. Cooper says it is currently investigating the potential compromise of customer data, and that it will notify all those whose data might have been impacted by the attack.
Mr. Cooper told SecurityWeek that it has already warned customers via email, website, social media posts, and its automated phone system of the incident, and that it will provide regular updates as the investigation into the matter advances.
“Customers who have tried or need to make payments will not incur fees, penalties or negative credit reporting as we work to resolve this issue,” the company also said.
Customers are advised to use Mr. Cooper’s text messaging platform for communication with their loan team.
The company has not provided details on the type of cyberattack it fell victim to, but taking systems offline is the typical response to a ransomware attack.
Headquartered in the Dallas, Texas, area, Mr. Cooper is one of the largest mortgage servicers in the US, with approximately 4.3 million customers.
Related: Clorox Blames Damaging Cyberattack for Product Shortage
Related: Healthcare Organizations Hit by Cyberattacks Last Year Reported Big Impact, Costs
Related: Australian Energy Software Firm Energy One Hit by Cyberattack













