CISO Strategy

LinkedIn Hires Former Twitter Security Chief Lea Kissner as New CISO

Lea Kissner replaces Geoff Belknap as Chief Information Security Officer (CISO) at Microsoft-owned LinkedIn.

LinkedIn

Business social networking giant LinkedIn has appointed former Twitter security chief Lea Kissner as its new Chief Information Security Officer (CISO).

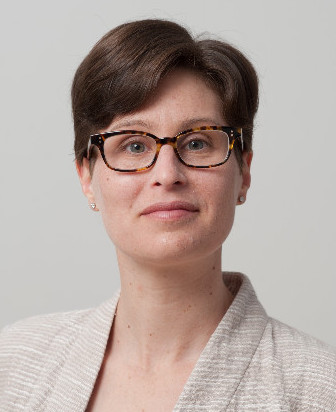
Lea Kissner Replaces Geoff Belknap as LinkedIn CISO.

Kissner, who departed Twitter after the Elon Musk acquisition, will be tasked with leading LinkedIn’s security and privacy strategy, ensuring the protection of LinkedIn’s member and customer data.

Kissner replaces Geoff Belknap, who recently moved into a separate leadership role at Microsoft, which owns LinkedIn.

Based in San Francisco, Kissner has been a prominent cybersecurity practitioner at several well known tech firms. Kissner was at Google for 12 years and left as global lead of privacy technology. After that came a move through some of the biggest firms in technology: HUMU (chief privacy officer), Zoom (security and privacy consultant), Apple (director of engineering), Twitter (starting as head of privacy engineering and becoming CISO and VP of Engineering), and then as CISO at Lacework.

Kissner shared the news on LinkedIn Wednesday. “Speaking as a heavy LinkedIn user I know that what we do here matters and I take that responsibility seriously,” Kissner posted. “ I’m an engineer (and cryptographer) by training and I believe that great security not only protects us but makes our systems work better and more robustly.”

Related: CISOs in Cloud-based Services Discuss the Process of Leadership

Related: Twitter Security Chief Resigns as Musk Sparks ‘Deep Concern’

Advertisement. Scroll to continue reading.

Related Content

Artificial Intelligence

The state-sponsored hackers targeted hundreds of organizations and gained privileged access to some environments.

Artificial Intelligence

Microsoft says companies should treat AI agents as insiders, and is adding controls that grant access per task and tighten it as an agent’s...

Vulnerabilities

In addition to RCE flaws, Microsoft fixed multiple information disclosure bugs and a security bypass issue in Office.

CISO Conversations

James Robinson never planned a cybersecurity career — seven companies and one deputy CISO role later, he leads security at Netskope.

Cybercrime

Backed by a federal court order, Microsoft and Health-ISAC seized domains powering YAM Store, CoGUI, and Iron Man.

Vulnerabilities

The most important is CVE-2026-96951, a security feature bypass flaw in Windows that has been exploited in the wild.

Cybercrime

Hackers used the account, which has 13 million followers, to amplify a Clippy-themed cryptocurrency account.

CISO Strategy

SecurityWeek seeks original, vendor-neutral presentations that help cybersecurity leaders navigate emerging threats, strengthen resilience, and address the strategic challenges facing today’s enterprise security programs.

Copyright © 2026 SecurityWeek ®, a Wired Business Media Publication. All Rights Reserved.

Exit mobile version