
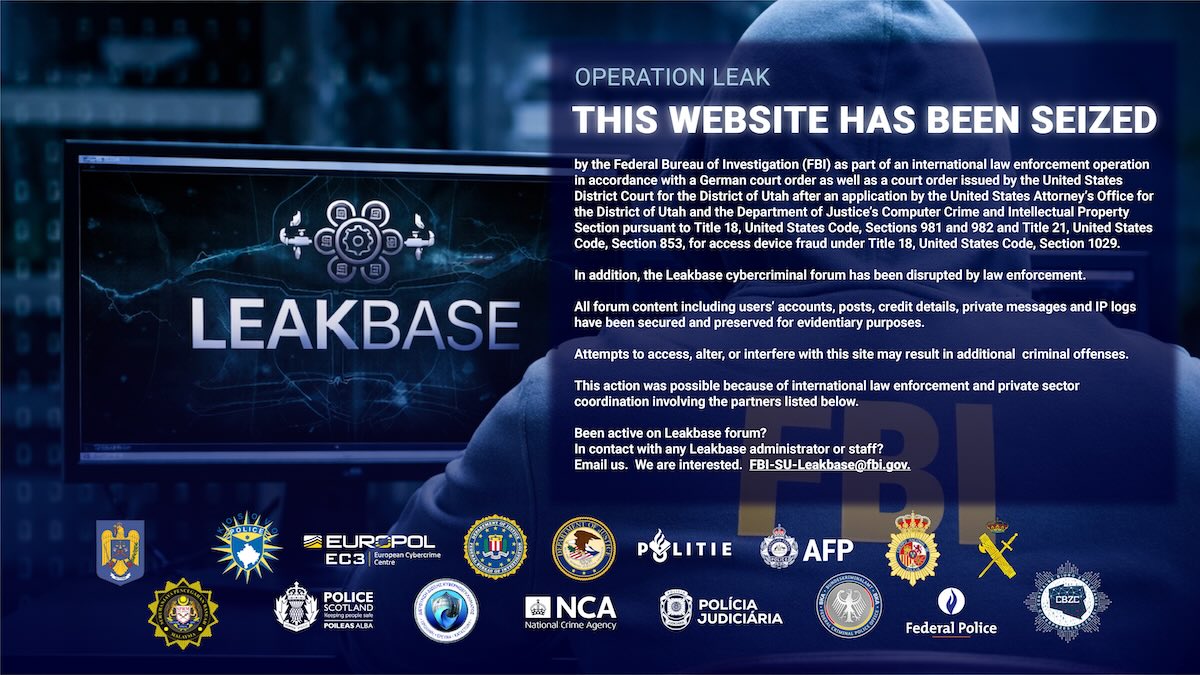
The popular cybercrime forum LeakBase has been shut down as part of an international law enforcement action named Operation Leak.
LeakBase had been active since 2021 and in December 2025 it had roughly 142,000 registered users, who sold and bought stolen information, including account credentials, personally identifiable information, payment card data, and bank account details.
As part of Operation Leak, law enforcement shut down two domains used by the forum and seized the LeakBase database. Seizure of the database enabled the identification of ‘multiple’ users.
Evidence collected by investigators included user account details, forum posts, private messages, and IP logs. Europol said the forum had approximately 215,000 private messages and 32,000 posts.
“A credit-based economy and reputation-driven user system helped build trust among offenders and sustain a thriving underground forum,” Europol explained.
The EU police agency also pointed out that “one of the forum’s notable internal rules prohibited the sale or publication of any data related to Russia”, hinting at the origin of LeakBase’s operators.
Law enforcement agencies from North America, Europe, and the APAC region have taken part in the operation.
Officers arrested suspects, and carried out house searches and knock-and-talk interventions. Unspecified measures were taken against 37 of the forum’s most active users.
The seizure of LeakBase was announced the same day that Europol, Microsoft, and several cybersecurity companies announced the takedown of the Tycoon 2FA phishing platform.
Related: SystemBC Infects 10,000 Devices After Defying Law Enforcement Takedown
Related: RaccoonO365 Phishing Service Disrupted, Leader Identified
Related: 1,000+ Servers Hit in Law Enforcement Takedown of Rhadamanthys, VenomRAT, Elysium






