
DebugBear says its DNS records were compromised via its domain registrar, and early findings show a single customer was targeted.
Hi, what are you looking for?

DebugBear says its DNS records were compromised via its domain registrar, and early findings show a single customer was targeted.
The FBI has officially pinned the $6 billion Binance hack on North Korea’s TraderTraitor as the attackers launder the stolen crypto.
CISA has added CVE-2026-111357 and CVE-2026-118527 to its KEV catalog after the Ivanti VPN flaws were chained in zero-day attacks.
The startup maps how identities, assets and vulnerabilities connect, and uses AI agents to find and fix risky combinations of issues.
A US court sentenced Syrian hacker Ahmad Umar Agha to 42 months for pro-Assad attacks on media, businesses, and government entities.
Over 22.6 million exposed instances are potentially affected by the critical PHP flaws that have been targeted for over a week.
Noteworthy stories that might have slipped under the radar: Iran eyed in military freezer hacks, Copenhagen University breach, AI-powered malware.
As organizations eliminate passwords, attackers will adapt. Instead of attacking the authenticator directly, they will look for opportunities around it.
It allowed customers to host hack-for-hire services, supported ransomware and infostealer operators, and accepted crypto payments.
Threat actors are attempting to exploit a high-severity unauthenticated race condition leading to remote code execution.
Drupal says a highly critical Commerce Core access bypass is exploited in the wild and urges store owners to audit their orders.
Malicious code linked to a website monitoring tool was designed to hijack logged-in Polymarket sessions and siphon user funds.
Tracked as CVE-2026-97229, the bug allows unauthenticated attackers to execute arbitrary code on the server.
An integer overflow tracked as CVE-2026-111585 could be used to execute arbitrary code on the viewer’s system.
Blockchain analysts link the record crypto theft to North Korean hackers, as Binance probes a possibly compromised engineer laptop.
Risk managers are trained to spot weak signals, plan for disruption and make hard decisions under uncertainty. But the discipline looks different when the risk is not a system or an enterprise, but you.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
Using thousands of hijacked accounts, the wfx-loot campaign planted a CI secret stealer that ran in over 1,800 GitHub repositories.


Created by Zerto and Kashya veterans, the startup has launched a platform designed to recover whole cloud applications.
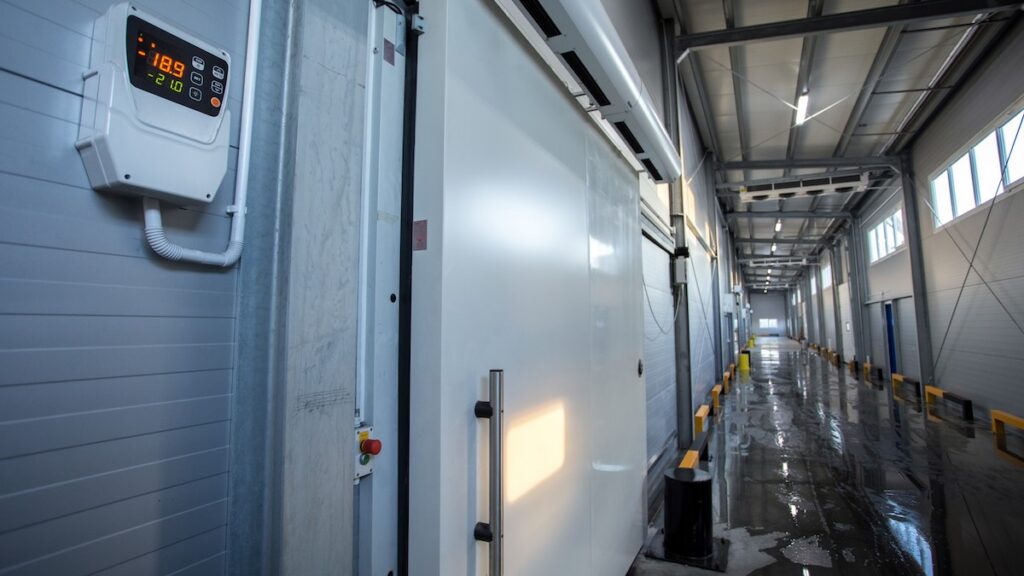
Vulncheck disclosed 14 vulnerabilities affecting Copeland XWEB EVO controllers, including two that threat actors quickly targeted.