
The security defects could allow attackers to bypass authorization and gain root access to devices.
Hi, what are you looking for?

The security defects could allow attackers to bypass authorization and gain root access to devices.
Apple has patched Bluetooth and AirPlay pairing flaws, iMessage vulnerabilities, and an exploited Brotli bug across its platforms.
CVE-2026-124194 is the Outlook zero-day for which Microsoft says it’s aware of active exploitation.
Adobe has fixed vulnerabilities in AEM, Premiere, Photoshop, After Effects, Connect, Audition, Dimension, Content Credentials SDK, and Media Encoder.
SBOM pioneer Allan Friedman joined the SecurityWeek Podcast to discuss why knowing what is inside software is only the beginning, how AI is complicating software supply chain visibility, and what organizations should be doing with SBOM data once they have it.
Google opened Carbon to paying developers and businesses as DeepMind used agents built on it to prove libsignal security guarantees.
The cybersecurity startup deploys a dedicated guardian agent for every AI agent in an organization’s environment.
SAP has published 42 new and updated security advisories, including nine that address critical-severity vulnerabilities.
Hackers used compromised Qubole IAM credentials to steal customer files, secrets, keys, environment variables, and credentials.
Anthropic says Mythos 5.2 improves vulnerability discovery while showing a lower tendency to escape sandboxes in controlled tests.
Attackers could exploit the flaws for remote code execution, credential theft, and administrator account creation.
CISA has added CVE-2026-123218 and CVE-2026-116779 to KEV, urging federal agencies to patch them within three days.
France summoned the Iranian ambassador and said it would seek European sanctions against those responsible for the attack
The high-severity use-after-free in Chrome’s XML component was reported anonymously on November 6 and is already exploited in attacks.
Online fashion retailer Revolve has told regulators that the September cyberattack affected more than 1.5 million individuals.
Threat actors are exploiting the four-flaw chain to hack the Plex Media Server application on QNAP NAS devices.
The leading global conference series for Operations, Control Systems and IT/OT Security professionals to connect on SCADA, DCS PLC and field controller cybersecurity.
Using thousands of hijacked accounts, the wfx-loot campaign planted a CI secret stealer that ran in over 1,800 GitHub repositories.


Created by Zerto and Kashya veterans, the startup has launched a platform designed to recover whole cloud applications.
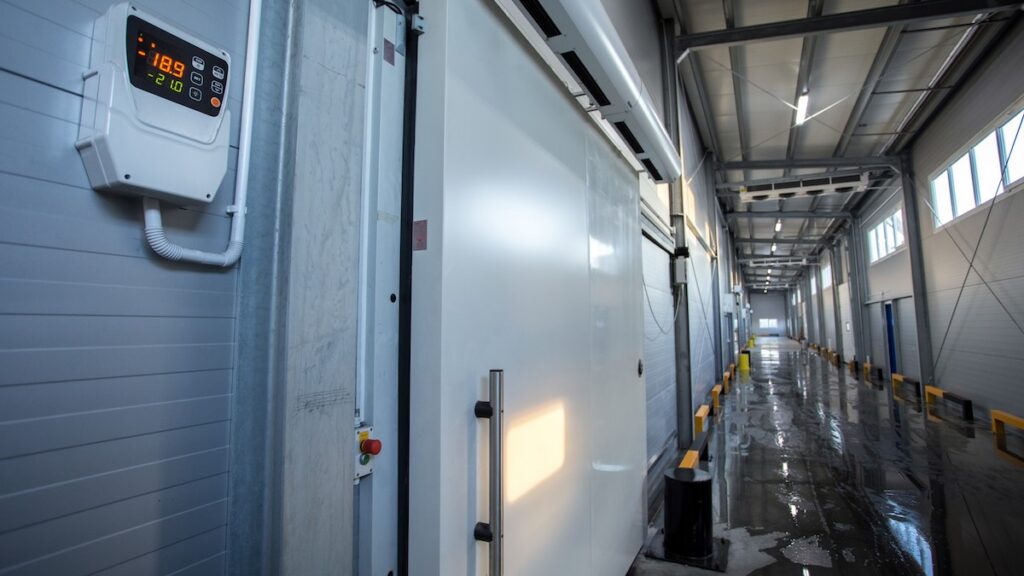
Vulncheck disclosed 14 vulnerabilities affecting Copeland XWEB EVO controllers, including two that threat actors quickly targeted.